Professional Security Services for Compliance, Risk Reduction & Cybersecurity Leadership
Advisory cybersecurity leadership and consulting to reduce risk, ensure compliance, and build resilient, audit-ready programs. Includes vCISO, penetration testing, and regulatory support for HIPAA, GLBA, and FFIEC.
Get clarity on risk, compliance, and priorities
Our cybersecurity consulting services help organizations identify risks, uncover vulnerabilities, and prioritize remediation based on real business impact. We deliver structured risk assessments, penetration testing, and compliance consulting aligned with regulatory and industry requirements.
Our professional security services include cybersecurity leadership, information security consulting, risk assessments, penetration testing, and compliance audit services designed to reduce risk and ensure regulatory readiness.
Security Leadership & Advisory Services
Executive cybersecurity leadership that aligns IT strategy, governance, and compliance with business objectives and regulatory expectations.
Virtual CISO (vCISO)
Fractional security leadership to build and mature your security program. NIST CSF-aligned governance with cybersecurity risk management.
Virtual CIO (vCIO)
Strategic IT planning, budgeting, and vendor governance to support stability and growth. Focused on IT-business alignment and operational efficiency.
Interim / On‑Demand CISO
Keep momentum while you recruit. Flexible monthly leadership or pre‑purchased hours for surge support. Ensures continuity during audits, incidents, or leadership transitions.
Program & Roadmap Development
Prioritized, budget-aligned security program roadmap and policies that improve maturity, satisfy auditors, and align with long-term cybersecurity risk management goals.
Security Testing, Risk & Compliance Services
Independent security validation services that identify vulnerabilities, assess risk, and ensure compliance with regulatory frameworks.
Ransomware Gap Assessment
A structured ransomware risk assessment based on NIST IR 8374 to evaluate prevention, detection, response, and recovery capabilities.
Penetration Testing
Simulated cyberattacks across networks, applications, and cloud environments to identify exploitable vulnerabilities and validate security controls.
Risk Assessments
Tailored risk assessment cybersecurity services, including third-party risk assessment, mapped to HIPAA, GLBA, FFIEC, SWIFT, and FERPA, with remediation ownership and timelines.
Compliance Audits & Attestations
Independent compliance audit services and security control reviews aligned with regulatory frameworks, supporting audit readiness and executive reporting.
TESTIMONIAL
“TorchLight has been more than a vendor to our multi‑branch credit union; they’re a partner. We started with a security assessment and gap analysis in 2007 and have continued to grow with their guidance across strategy, compliance, and operations.”
– Annettee Babb, CEO, Primesource Credit Union
Why Organizations Choose TorchLight
We provide cybersecurity consulting services and security leadership designed for regulated industries where cybersecurity risk management, compliance, and audit readiness are critical. Our approach combines strategic advisory, technical validation, and regulatory alignment to help organizations reduce risk and improve cybersecurity maturity.
- Expertise in regulated industries (financial, healthcare, government)
- Execution-focused cybersecurity advisory
- Alignment with HIPAA, GLBA, FFIEC, and NIST CSF
- Transparent executive communication
- Continuous security maturity improvement
Our approach complements internal teams and enhances existing managed security services capabilities.
Our clients rely on us to improve audit readiness, strengthen security posture, and maintain continuous compliance in highly regulated environments.
Frequently Asked Questions
What are cybersecurity consulting services?
Cybersecurity consulting services help organizations identify risks, implement security controls, and achieve compliance with industry standards.
What do vCISO services include?
A vCISO provides strategic cybersecurity leadership, including risk management, compliance alignment, and security program development.
What is included in a cybersecurity risk assessment?
A cybersecurity risk assessment identifies vulnerabilities, evaluates threats, and prioritizes remediation actions to reduce risk.
How often should risk assessments be done?
Risk assessments are typically conducted annually or after significant infrastructure, system, or regulatory changes. More frequent assessments may be required for highly regulated or high-risk environments.
What is penetration testing?
Penetration testing simulates real-world cyberattacks to identify exploitable vulnerabilities in networks, applications, and cloud environments. It helps organizations validate security controls and prioritize remediation before attackers can exploit weaknesses.
What is a ransomware risk assessment?
A ransomware risk assessment evaluates how prepared an organization is to prevent, detect, and recover from ransomware attacks.
Why do organizations need compliance audit services?
Compliance audit services validate that security controls meet regulatory standards like HIPAA, GLBA, and FFIEC.
What are FFIEC compliance services?
FFIEC compliance services help financial institutions meet regulatory cybersecurity and risk management requirements.
How does HIPAA security consulting help organizations?
HIPAA security consulting ensures healthcare organizations meet data protection and compliance requirements.
What industries need security services most?
Highly regulated industries such as financial services, healthcare, government, and education.
Latest Insights & Blog
Expert insights on cybersecurity, compliance, and IT strategy.
-
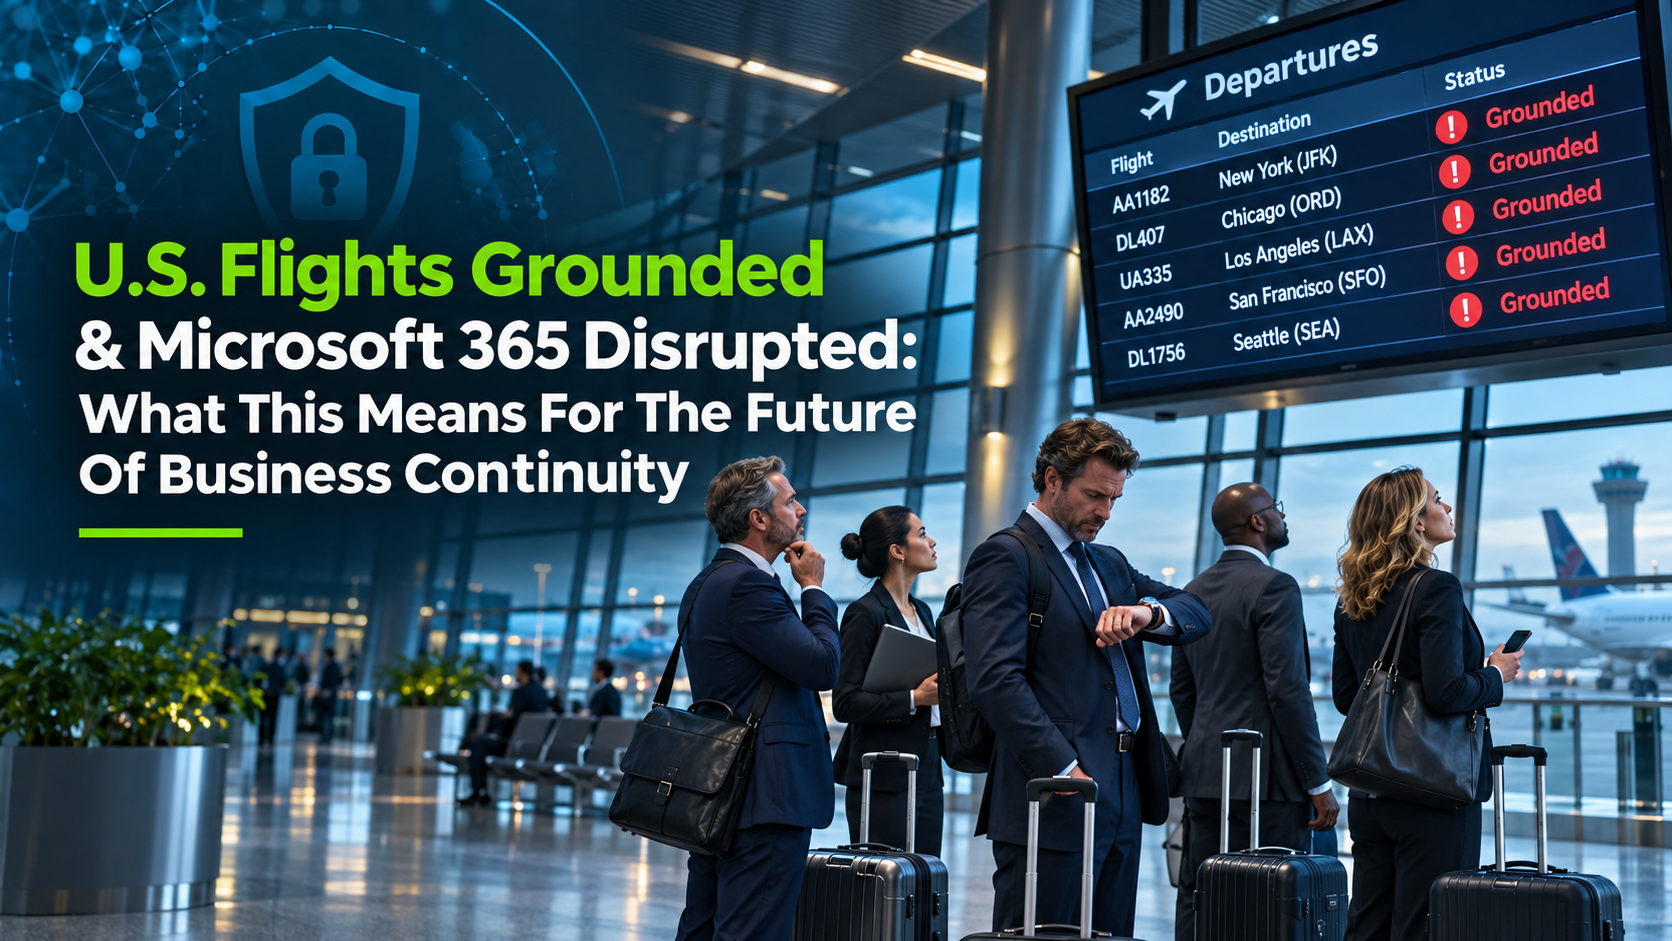
U.S. Flights Grounded & Microsoft 365 Disrupted: What This Means For The Future Of Business Continuity
Two major infrastructure disruptions in less than 24 hours are exposing a critical weakness in traditional business continuity planning. As Microsoft 365 experienced widespread service disruptions and the FAA grounded departing flights nationwide, regulated organizations were reminded that backups and cybersecurity alone cannot guarantee operational resilience. Here’s what business leaders should revisit before the next…
-
Claude Fable 5.2 and Mythos 5.2: What the New AI Capabilities Mean for Business Cybersecurity
Anthropic’s release of Claude Fable 5.2 and Mythos 5.2 demonstrates advances in AI-assisted vulnerability discovery. Combined with Microsoft’s recent findings on automated cloud attacks, the release raises important questions for small and mid-sized businesses. Explore five cybersecurity priorities and a practical 30-day plan for evaluating your organization’s exposure, security monitoring, and readiness. Copy excerpt
-
In-House SOC vs. Managed SOC: What 24/7 Security Really Costs
Hiring another analyst won’t automatically deliver 24/7 cybersecurity coverage. Compare the real cost of building an in-house SOC against managed and co-managed security, using verified workforce research and federal compensation data. A practical 2027 budgeting guide for executives and IT leaders in regulated organizations. Copy excerpt