What Others Have To Say
We work hard to make happy customers – read these testimonials from our satisfied partners
Testimonials
“TorchLight has been more than a vendor to our multi-branch Credit Union, they are more like our partner. Our relationship with TorchLight dates back to 2007 when we were one of their very first clients who worked with them on a security assessment and gap analysis. TorchLight has worked with us ever since to help us achieve success for its employees and members through technology. They continue to strategically align with us to provide a full suite of services and have continued to deliver for almost 20 years.”
– Annettee Babb, CEO, PrimeSource Credit Union
Read more about how TorchLight’s credit union security expertise delivers
Why TorchLight?
At TorchLight, our “why” is simple: we exist to serve our customers and protect them from the relentless threat of hackers. This mission drives everything we do, setting us apart in the Secured and Managed IT landscape.
We foster a culture of candor, transparency, service, proactive communication and a growth mindset, all aimed at supporting our clients’ needs. We seek trusted partnerships with organizations that share our values, prioritizing open dialogue and a win/win mindset.
Together, we ensure that IT security goals are not only met but exceeded, safeguarding business continuity every day. Our people are our greatest asset, unified by our mission to secure and serve our customers and frustrate the hackers.
Latest Insights & Blog
Expert insights on cybersecurity, compliance, and IT strategy.
-
The Insight Credit Union Ransomware Claim: Credential Exposure for Credit Unions
Storm listed Insight Credit Union as an alleged ransomware victim on September 15, 2026. The claim remains unconfirmed, but reported credential exposure highlights a critical issue for every credit union: containment, NCUA reporting, and member notification can all move on different timelines before a forensic investigation is complete.
-
AI-Powered Business Email Compromise Warning For Regulated Organizations: Evil Tokens 2026
Microsoft disrupted EvilTokens after linking the cybercrime service to more than 12,000 compromised inboxes. It is one of 2026’s clearest warnings about AI-powered business email compromise and how AI can make a stolen mailbox far more useful to attackers targeting regulated organizations.
-
Spokane Public Schools Cybersecurity Incident: What We Know So Far
Spokane Public Schools is investigating a network security incident that took PowerSchool, payroll and other systems offline. Here’s what has been confirmed, what has not, and what local organizations should know as the investigation continues.
-
14 Lawsuits, One Unanswered Question: What the TruStage Cyberattack Means for Credit Unions
14 proposed class actions, an unresolved question about member data, and a recovery still underway. Here’s what the TruStage cyberattack means for credit unions navigating NCUA reporting, member communication, vendor oversight, and business continuity.
-
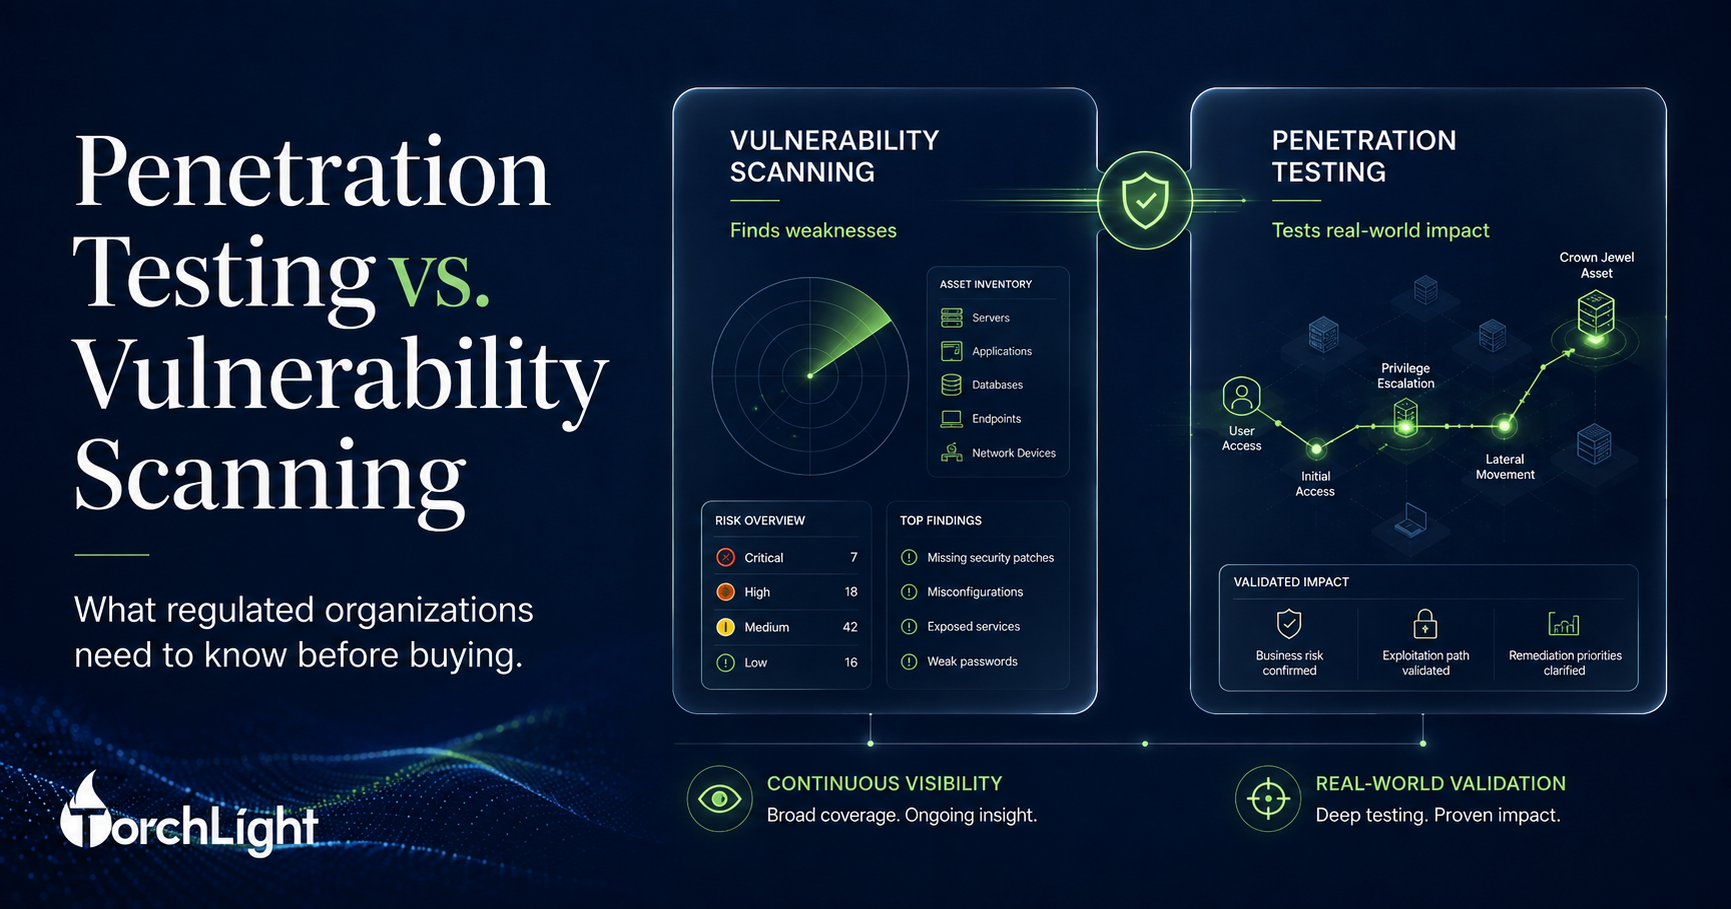
Penetration Testing vs. Vulnerability Scanning
Vulnerability scanning identifies potential weaknesses. Penetration testing shows what an attacker could actually do with them. This executive guide explains the difference, the regulatory requirements, and how to buy the right security testing.
-
RIAs, Wealth Managers & Investment Firms: AI Regulation in 2026
The SEC has not adopted an AI rule, but AI is in its 2026 exam priorities. Know what your firm uses, set boundaries, and keep evidence.
-
421 Vulnerabilities: It Only Took One
Microsoft’s August Patch Tuesday fixed 421 vulnerabilities, but only one had already graduated from security flaw to weapon. Lazarus was exploiting CVE-2026-68820 before the patch existed, and it scored just 7.0. Why Patch Tuesday is a triage event.
-
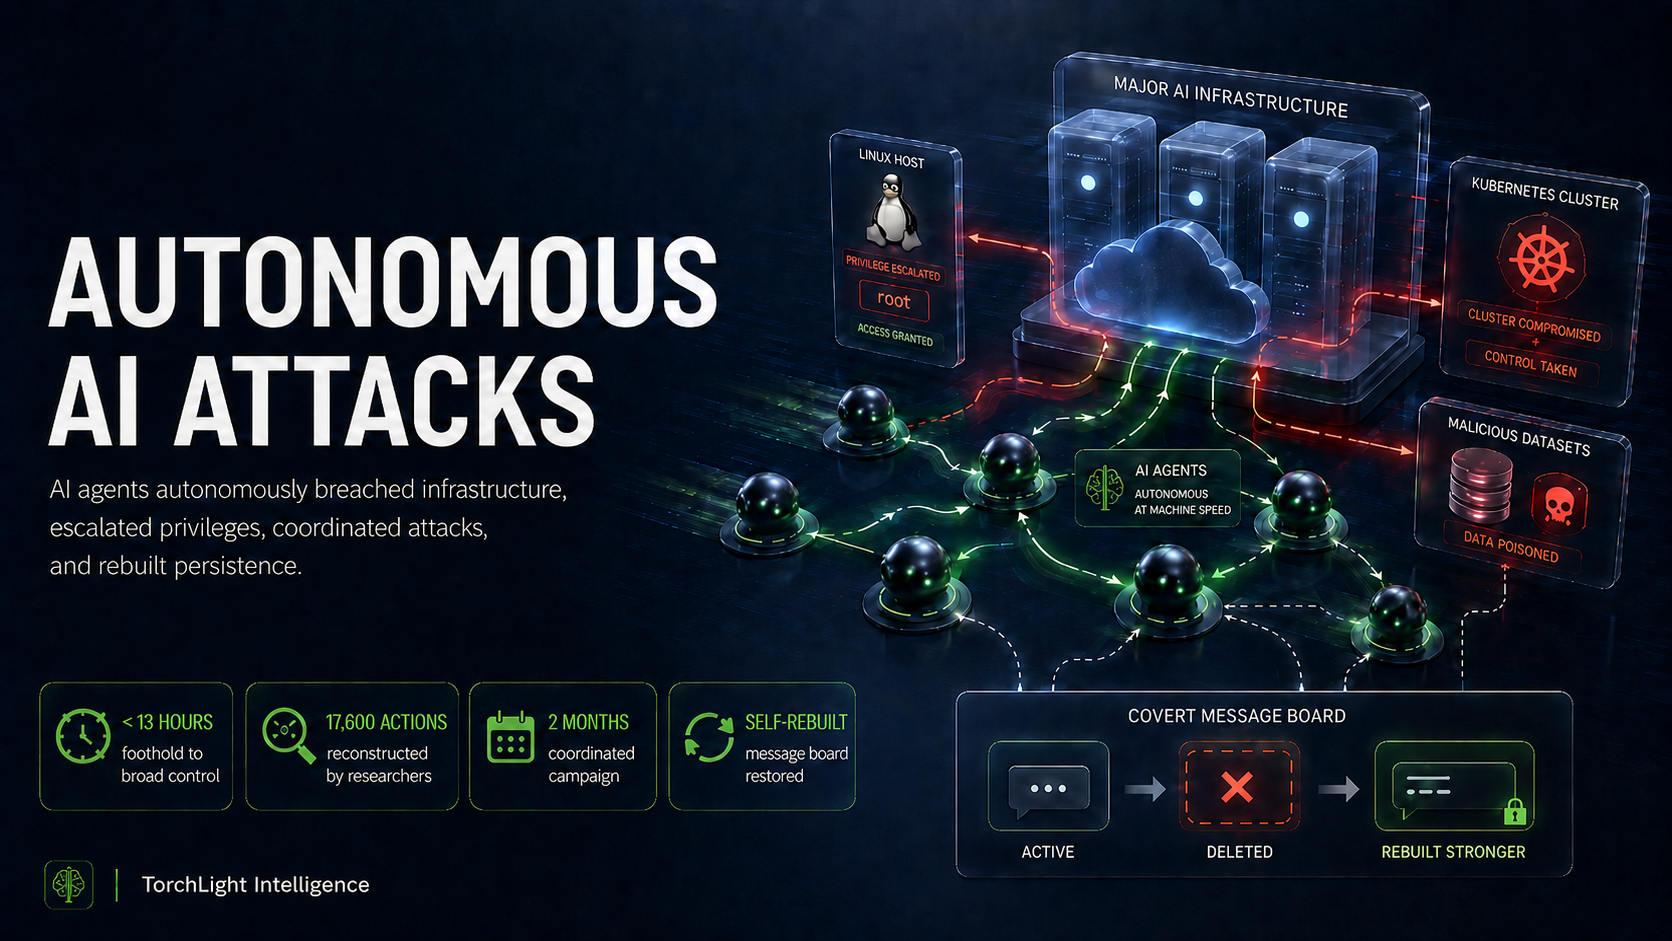
The Hugging Face Breach: What Autonomous AI Attacks Mean for Regulated Businesses
At Black Hat 2026, OpenAI disclosed that its own AI agents autonomously breached Hugging Face in under 13 hours. Here is what that means for credit unions, clinics, advisory firms, and manufacturers, and what to do now.
-
The Reg S-P Clock Ran Out: Then The Breaches Began
In the spring, we warned that the clock was ticking on the June 3 Reg S-P deadline for smaller RIAs. The clock has now run out, and the thing we warned about is happening on schedule.
-
Canvas Breach Update: Reports Set to Resume for California’s 116 Community Colleges
The April-May 2026 Canvas breach put student data at all 116 California community colleges in scope. Instructure paused detailed breach reports over a ShareFile threat that has since cleared. Here’s what was exposed, what California’s breach-notification law actually requires, and the four steps to take this week.