Credit Union Compliance Confidence
How One Credit Union Went From Cyber Insurance Cancellation to Zero NCUA Cybersecurity Findings in 90 Days
The step-by-step transformation that eliminated emergency IT calls during member service hours and restored board confidence.
Cyber Insurance Canceled
TorchLight received a phone call from a Credit Union CEO facing a crisis. Their insurance company had just canceled coverage following a failed NCUA audit and ongoing technical issues that disrupted member services. The final straw came when their failing firewall caused operational downtime on a payroll Friday.
The board was asking tough questions, but the CEO had been constrained by limited budget approval. Within 90 days, TorchLight transformed their operations.
- Upgraded their network infrastructure for bulletproof reliability
- Integrated previously ignored M365 licenses into daily business operations, including Teams, Outlook, SharePoint, and OneDrive
- Resolved all outstanding NCUA audit issues
- Restored the Credit Union to an insurable state
Secured & Managed IT by TorchLight
Our Secured & Managed IT Brings Board Actualization Through Our Maslow Heirarchy of Needs Approach To Credit Union Compliance Confidence:
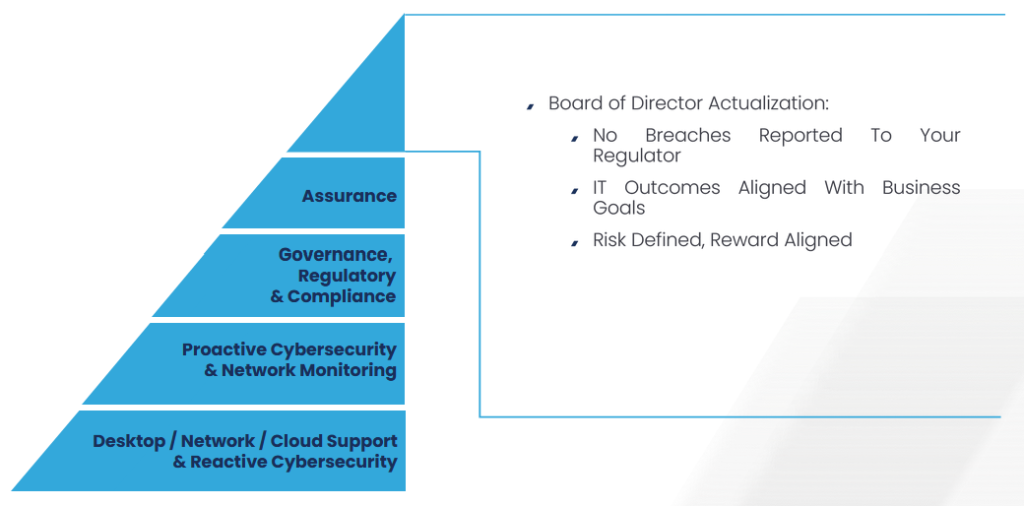
Board Actualization
- No Breaches To Report To Your Regulator
- IT Outcomes Aligned With Business Goals
- Risk Defined, Reward Aligned
Assurance
- Board Confidence That Controls And Oversight Actually Work
- If A Breach Were To Occur, Risk Communicated In Advance
- Act Swiftly To Recover, Contain Spread Immediately and Restore Operations Within Minutes
Governance, Regulatory and Compliance
- On Call Fractional Virtual Chief Information Security Officer
- Proactive Risk Awareness For Purpose Built Mitigations
- Board Level Reporting and Presentations By The vCISO
Proactive Cybersecurity and Network Monitoring
- 24/7/365 Human Powered Security & Network Operations Center
- DMARC, DNS and Email Spoofing Monitoring
- Desktop + Server Patching & Cloud + On-Prem Backups
- Customizable Security Awareness Training
- Dedicated Organizational Password Manager
- Integration with HR, Physical Access and Other Critical Systems
Desktop / Network / Cloud Support and Reactive Cybersecurity
- Patching + Backups
- Endpoint Detection + 24/7/365 Managed Incident Response
- Cloud Identity Detection + 24/7/365 Managed Incident Response
- Microsoft 365 Tenancy & License Management
- Predictable and Reliable Service Desk with Guaranteed SLA’s
What To Expect Working With TorchLight
Before: Downtime, user friction, customer headaches, technical debt, compliance dread.
After: Zero downtime, simplified business processes, increased compliance accountability with a predictable monthly budget.
We get Credit Unions. With more than 17 years of Managed Security & IT experience, along with testing, audits and consulting experience, we know what it takes to bring Board Self Actualization!
- Smooth on-boarding with a gradual implementation plan
- On Call vCISO to advise, consult and speak to your IT risks and help build Board awareness
- Predictable monthly cost that scales with confidence when it’s time to grow
- Maximize the value and full benefits with your M365 licensing
- Technical Liaison with your Processors, Integrators and Vendors
Get a Cybersecurity Compliance Assessment From a Certified Microsoft Solutions Partner for Security to Upgrade Your Credit Union to a Better Secured & Managed IT State with Compliance Confidence.
Why TorchLight?
At TorchLight, our “why” is simple: we exist to serve our customers and protect them from the relentless threat of hackers. This mission drives everything we do, setting us apart in the Secured and Managed IT landscape.
We foster a culture of candor, transparency, service, proactive communication and a growth mindset, all aimed at supporting our clients’ needs. We seek trusted partnerships with organizations that share our values, prioritizing open dialogue and a win/win mindset.
Together, we ensure that IT security goals are not only met but exceeded, safeguarding business continuity every day. Our people are our greatest asset, unified by our mission to secure and serve our customers and frustrate the hackers.
Latest Insights & Blog
Expert insights on cybersecurity, compliance, and IT strategy.
-
CISA Flags Exploited Backup Software: Can Your Business Continuity Plan Survive An Attack?
CISA’s October 2026 warning confirms attackers are exploiting vulnerabilities in backup management software. For CEOs, boards, and IT leaders, the bigger concern is business continuity: Could your organization still recover if both its primary systems and backup infrastructure were compromised? Here’s what leadership needs to know.
-
School District Vendor Risk Management: Why Education Needs Better Vendor Oversight
A school district can secure its own network and still face student-data exposure through a third-party vendor. Using California’s ETS breach as a case study, TorchLight examines vendor risk management, student privacy, and four practical questions school boards should be asking, with specific guidance for Washington and California education leaders.
-
When The Audit Ends, What Happens To Credit Union Member Data?
When an audit ends, sensitive member information may remain with the auditor for years. The Mercadien cybersecurity incident highlights why credit union leaders should review data retention, secure deletion, and vendor notification terms as part of existing oversight.
-
Spokane Public Schools Cybersecurity Incident: What We Know So Far
Spokane Public Schools now says it has reason to believe student and staff data was compromised in the September cybersecurity incident. The investigation remains ongoing as specialists work to determine what information was affected and who may need to be notified.
-
The Data Your AI Agent Reads Can Hijack It: What Regulated Organizations Need To Know After SalesBleed
SalesBleed showed how ordinary business data can become instructions to an AI agent with access to sensitive systems. For RIAs, the bigger question is whether leadership understands which AI tools are already operating, what they can access, and what authority they have. Here’s what firms should review now.
-
The Insight Credit Union Ransomware Claim: Credential Exposure for Credit Unions
Storm listed Insight Credit Union as an alleged ransomware victim on September 15, 2026. The claim remains unconfirmed, but reported credential exposure highlights a critical issue for every credit union: containment, NCUA reporting, and member notification can all move on different timelines before a forensic investigation is complete.
-
AI-Powered Business Email Compromise Warning For Regulated Organizations: Evil Tokens 2026
Microsoft disrupted EvilTokens after linking the cybercrime service to more than 12,000 compromised inboxes. It is one of 2026’s clearest warnings about AI-powered business email compromise and how AI can make a stolen mailbox far more useful to attackers targeting regulated organizations.
-
14 Lawsuits, One Unanswered Question: What the TruStage Cyberattack Means for Credit Unions
14 proposed class actions, an unresolved question about member data, and a recovery still underway. Here’s what the TruStage cyberattack means for credit unions navigating NCUA reporting, member communication, vendor oversight, and business continuity.
-
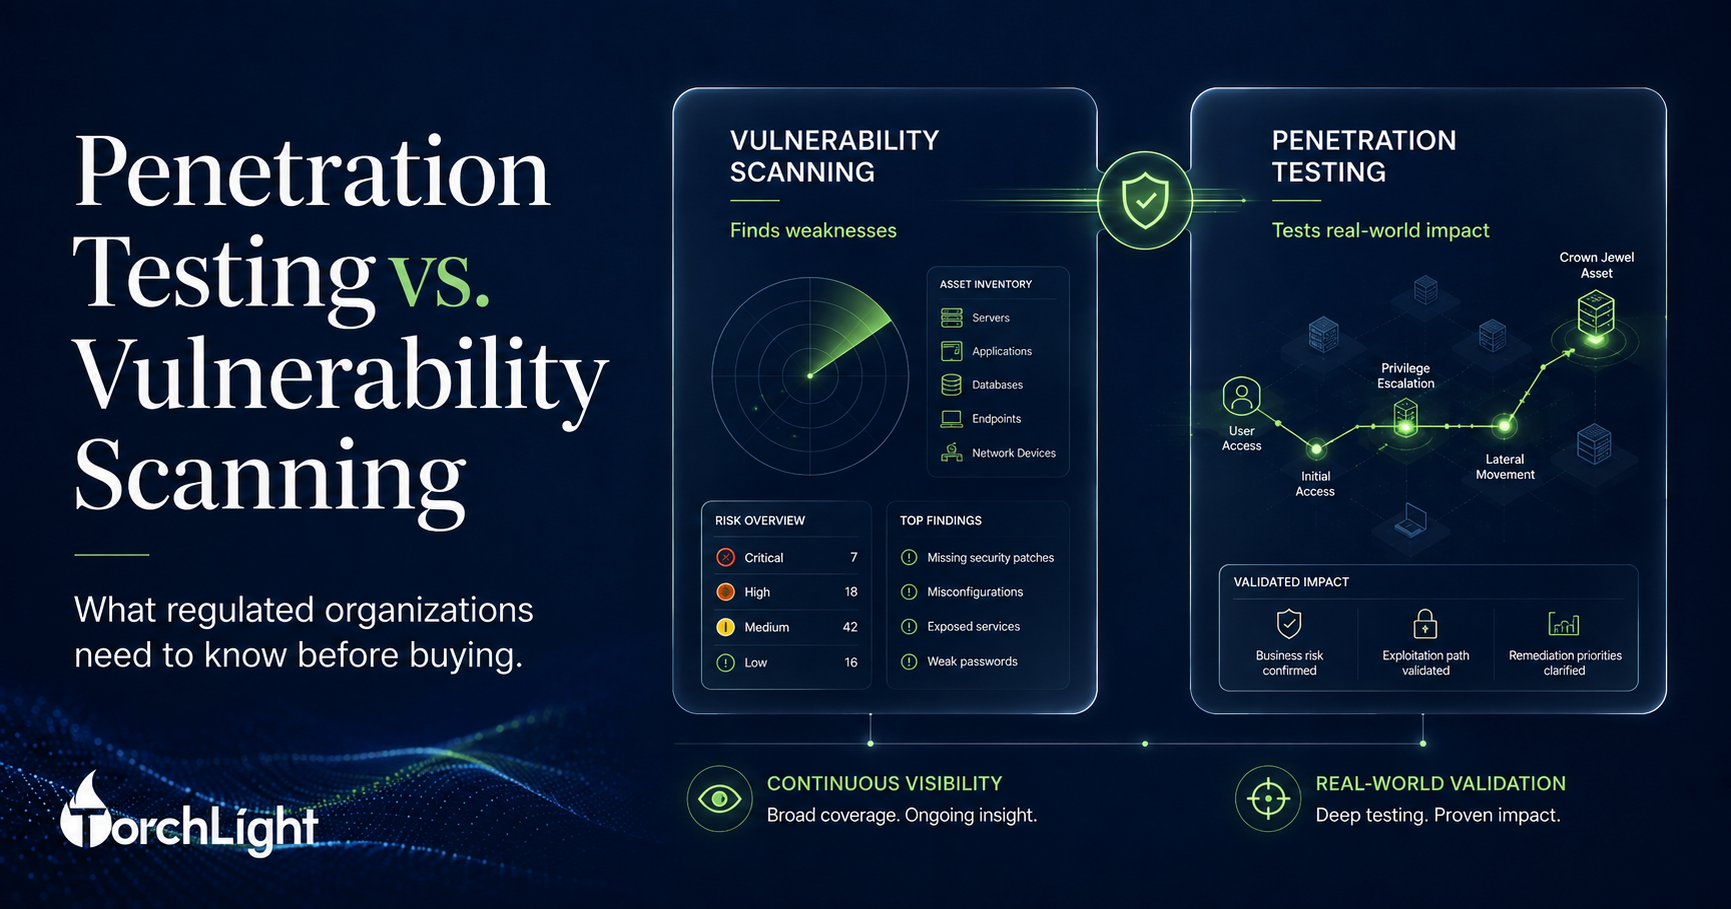
Penetration Testing vs. Vulnerability Scanning
Vulnerability scanning identifies potential weaknesses. Penetration testing shows what an attacker could actually do with them. This executive guide explains the difference, the regulatory requirements, and how to buy the right security testing.
-
RIAs, Wealth Managers & Investment Firms: AI Regulation in 2026
The SEC has not adopted an AI rule, but AI is in its 2026 exam priorities. Know what your firm uses, set boundaries, and keep evidence.