Fractional
vCISO & vCIO
Get experienced security and technology leadership built around your organization; your people, risk, regulatory obligations, budget, and systems. TorchLight helps connect board-level decisions to the processes behind them, without the overhead of another full-time executive role.
Talk With aFractional Leader
Advisory That Does More.
A roadmap and a quarterly presentation can be useful, but neither mean much when the advice is coming from someone that is disconnected from the systems, people, vendors, budgets, and regulatory pressure behind it.
TorchLight connects executive guidance with the technology environment, security program, regulatory obligations, vendors, budgets, and people responsible for doing the work.
That gives leadership something more useful than a strategy document. It creates continuity between the boardroom and the work being done behind the scenes.
Different Disciplines: One standard of accountability.
One Organization. One Technology Strategy.
Business priorities, technology, cybersecurity, compliance, and execution influence one another. Your fractional leadership model should reflect that.
The value is not simply having access to a vCISO or vCIO: It is preserving context from strategy all the way through execution.
The Person Advising Your Leadership Team Should Understand What Happens After the Meeting.
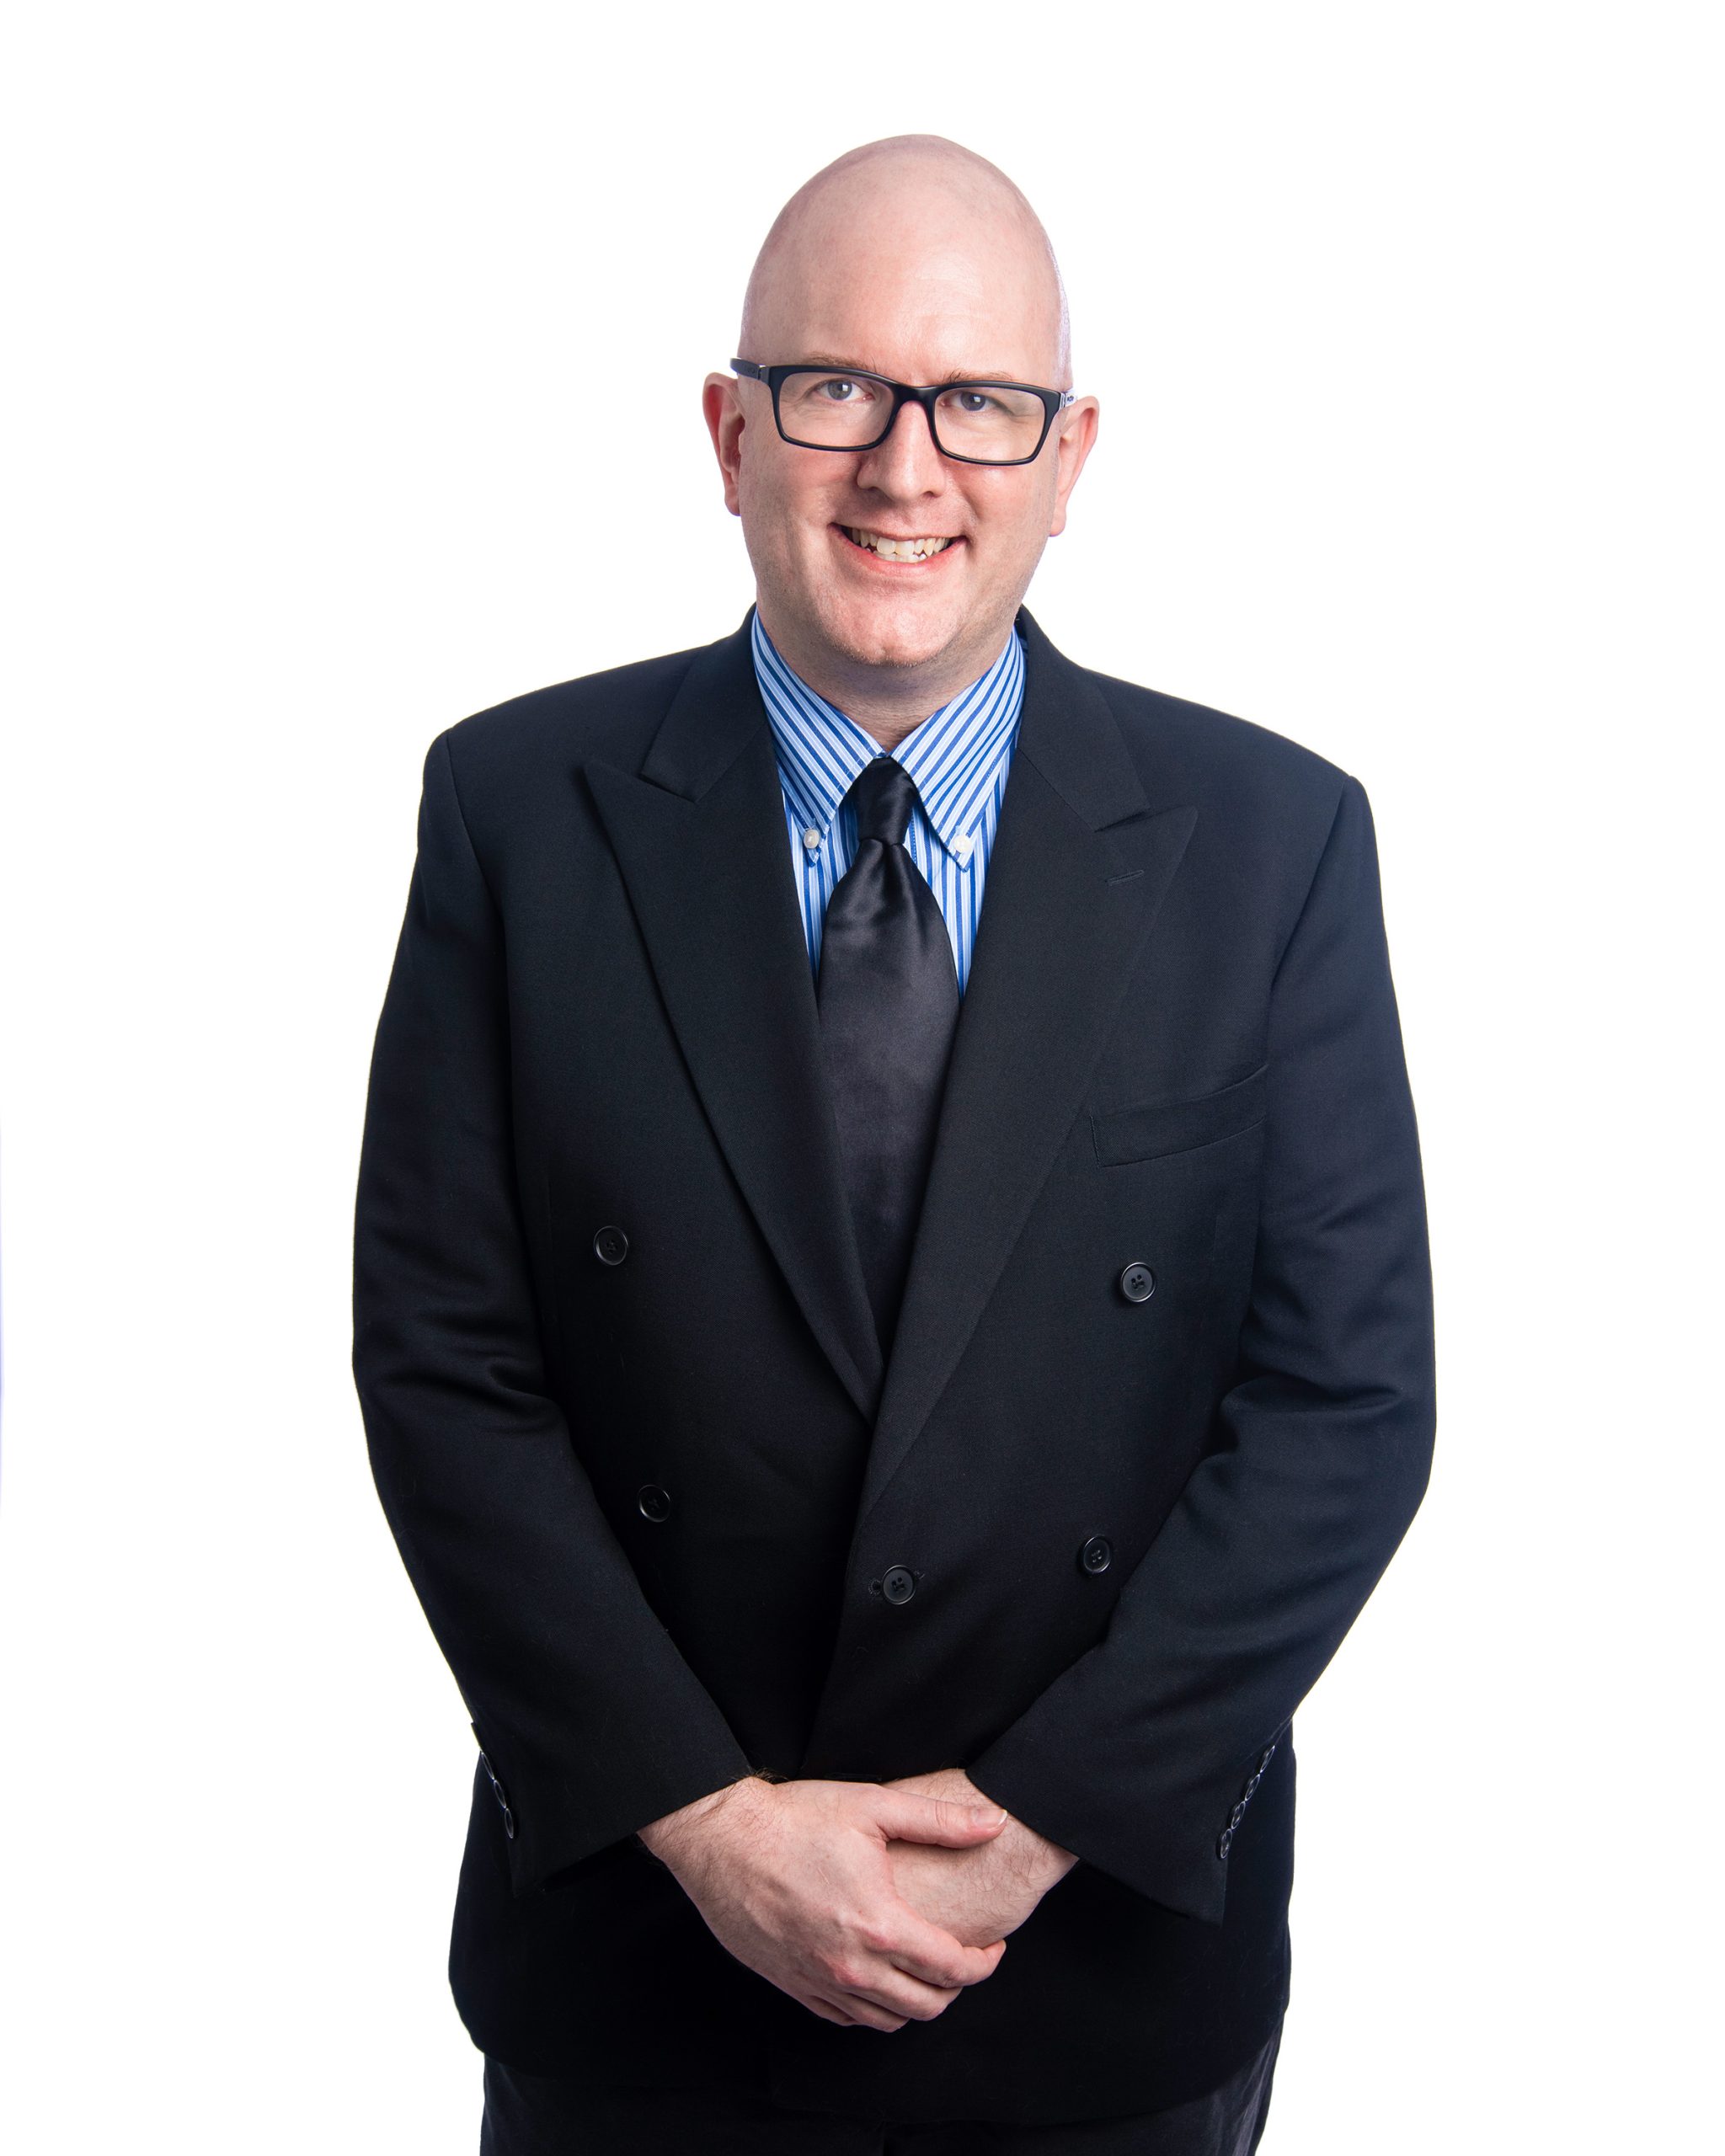
Gary Blosser · Executive Consultant & Principal Security Architect · TorchLightFractional leadership depends heavily on trust. The person helping your executives and board make technology and cybersecurity decisions needs to understand more than governance language and presentation slides.
Gary Blosser brings experience spanning executive security leadership, architecture, offensive security, penetration testing, incident response, digital forensics, threat intelligence, and enterprise consulting. That range matters when a strategic recommendation eventually has to become real technical work.
Trust Comes From Context.
Strong fractional leadership means knowing enough about the organization, its systems, its risks, and its people to explain why a decision matters; and understanding what it will take to carry that decision through.
“Jack of all information technology, master of security. ”
Leadership Built Around Your Organization.
Some organizations need an experienced voice in the room a few times each month. Others need someone actively steering the security program, working with vendors, preparing the board, and carrying initiatives forward between meetings.
TorchLight’s fractional vCISO and vCIO model is designed to accommodate both. The level of involvement can grow around your organization’s risk, regulatory pressure, internal resources, projects, and leadership needs.
That matters because the right level of leadership today may not be the right level six months from now. An examination, acquisition, modernization effort, incident, leadership transition, or major project can quickly change what your team needs.
You should be able to increase the depth of leadership when the work demands it, without having to redesign the entire relationship.
Different Organizations Need Different Depth.
These are examples of how TorchLight engagements can scale. They are useful starting points, not a substitute for understanding what your organization actually needs.
The common thread is not the number of hours. It is having an experienced leader close enough to your organization to understand the context behind the decisions. That is what makes fractional leadership valuable.
Leadership Where You Need It. Ownership Where It Matters.
Fractional leadership can be strategic, operational, temporary, or deeply embedded. The right model depends on where your organization needs experienced judgment today and where your internal team can confidently carry the work themselves. TorchLight can work across both sides of that line.
Virtual CISO Leadership
Executive security leadership for organizations that need someone capable of building, operating, explaining, and defending the information security program.
Virtual CIO Leadership
Technology strategy should connect investment decisions to what the organization is actually trying to accomplish.
Interim / On-Demand Leadership
Month-to-month leadership during a search or transition, plus block-hour support for surge needs, incidents, examinations, or board cycles.
Guided Toolkit & Internal-Team Support
Templates, playbooks, and evidence checklists your team can operate internally, with a fractional leader available when guidance or review is needed.
You Should Know Who to Call. And They Should Already Know Why You’re Calling.
Once fractional leadership becomes part of the organization, the important questions start to change. The conversation becomes less about finding someone who can answer and more about whether the person answering already understands the context.
Who Already Knows What the Board Is Worried About?
The next conversation should start with context, not another explanation of the organization.
Who Remembers Why This Decision Was Made?
Technology strategy gets stronger when the reasoning behind previous decisions stays connected to what happens next.
Who Can Explain the Risk Without Creating Panic?
Leadership needs clear business meaning, practical options, and enough technical depth to make a defensible decision.
Who Knows Which Vendor Actually Owns the Next Step?
Good leadership understands where internal teams, providers, vendors, and executives intersect.
Who Can Walk Into an Audit Without Starting From Zero?
Governance, evidence, risk decisions, and remediation should already have an owner before the examiner arrives.
Who Can Connect the Budget Request to Business Risk?
Security and technology investments become easier to evaluate when leadership can see what the investment changes.
Who Follows the Recommendation Through Execution?
Strategy should remain connected to action owners, vendors, technical teams, KPIs, and evidence.
Who Gets the Call Before the Situation Becomes a Crisis?
The strongest leadership relationship exists before the incident, examination, difficult project, or board question arrives.
The Entire Point Is Continuity.
Your fractional leader should retain the context behind the roadmap, the risks that have already been discussed, the decisions already made, and the work still in motion.
Good Fractional Leadership Should Feel Familiar Before It Feels Urgent.
The value of the relationship compounds over time. Your fractional leader becomes familiar with the environment, the internal team, the vendors, the board, the regulatory pressure, and the decisions already in motion.
That familiarity changes the conversation. Instead of beginning with “Can you get up to speed?” leadership can begin with “Here is what changed.”
When the stakes rise, that difference matters. The person helping lead the response is not meeting your organization for the first time.
Good fractional leadership should feel less like calling a consultant and more like calling a member of your leadership team.
An Extension of Leadership, Not Another Layer Between Leadership and IT.
The relationship works when executive guidance, technology strategy, security, compliance, and follow-through remain connected instead of being handed from one disconnected advisor to another.
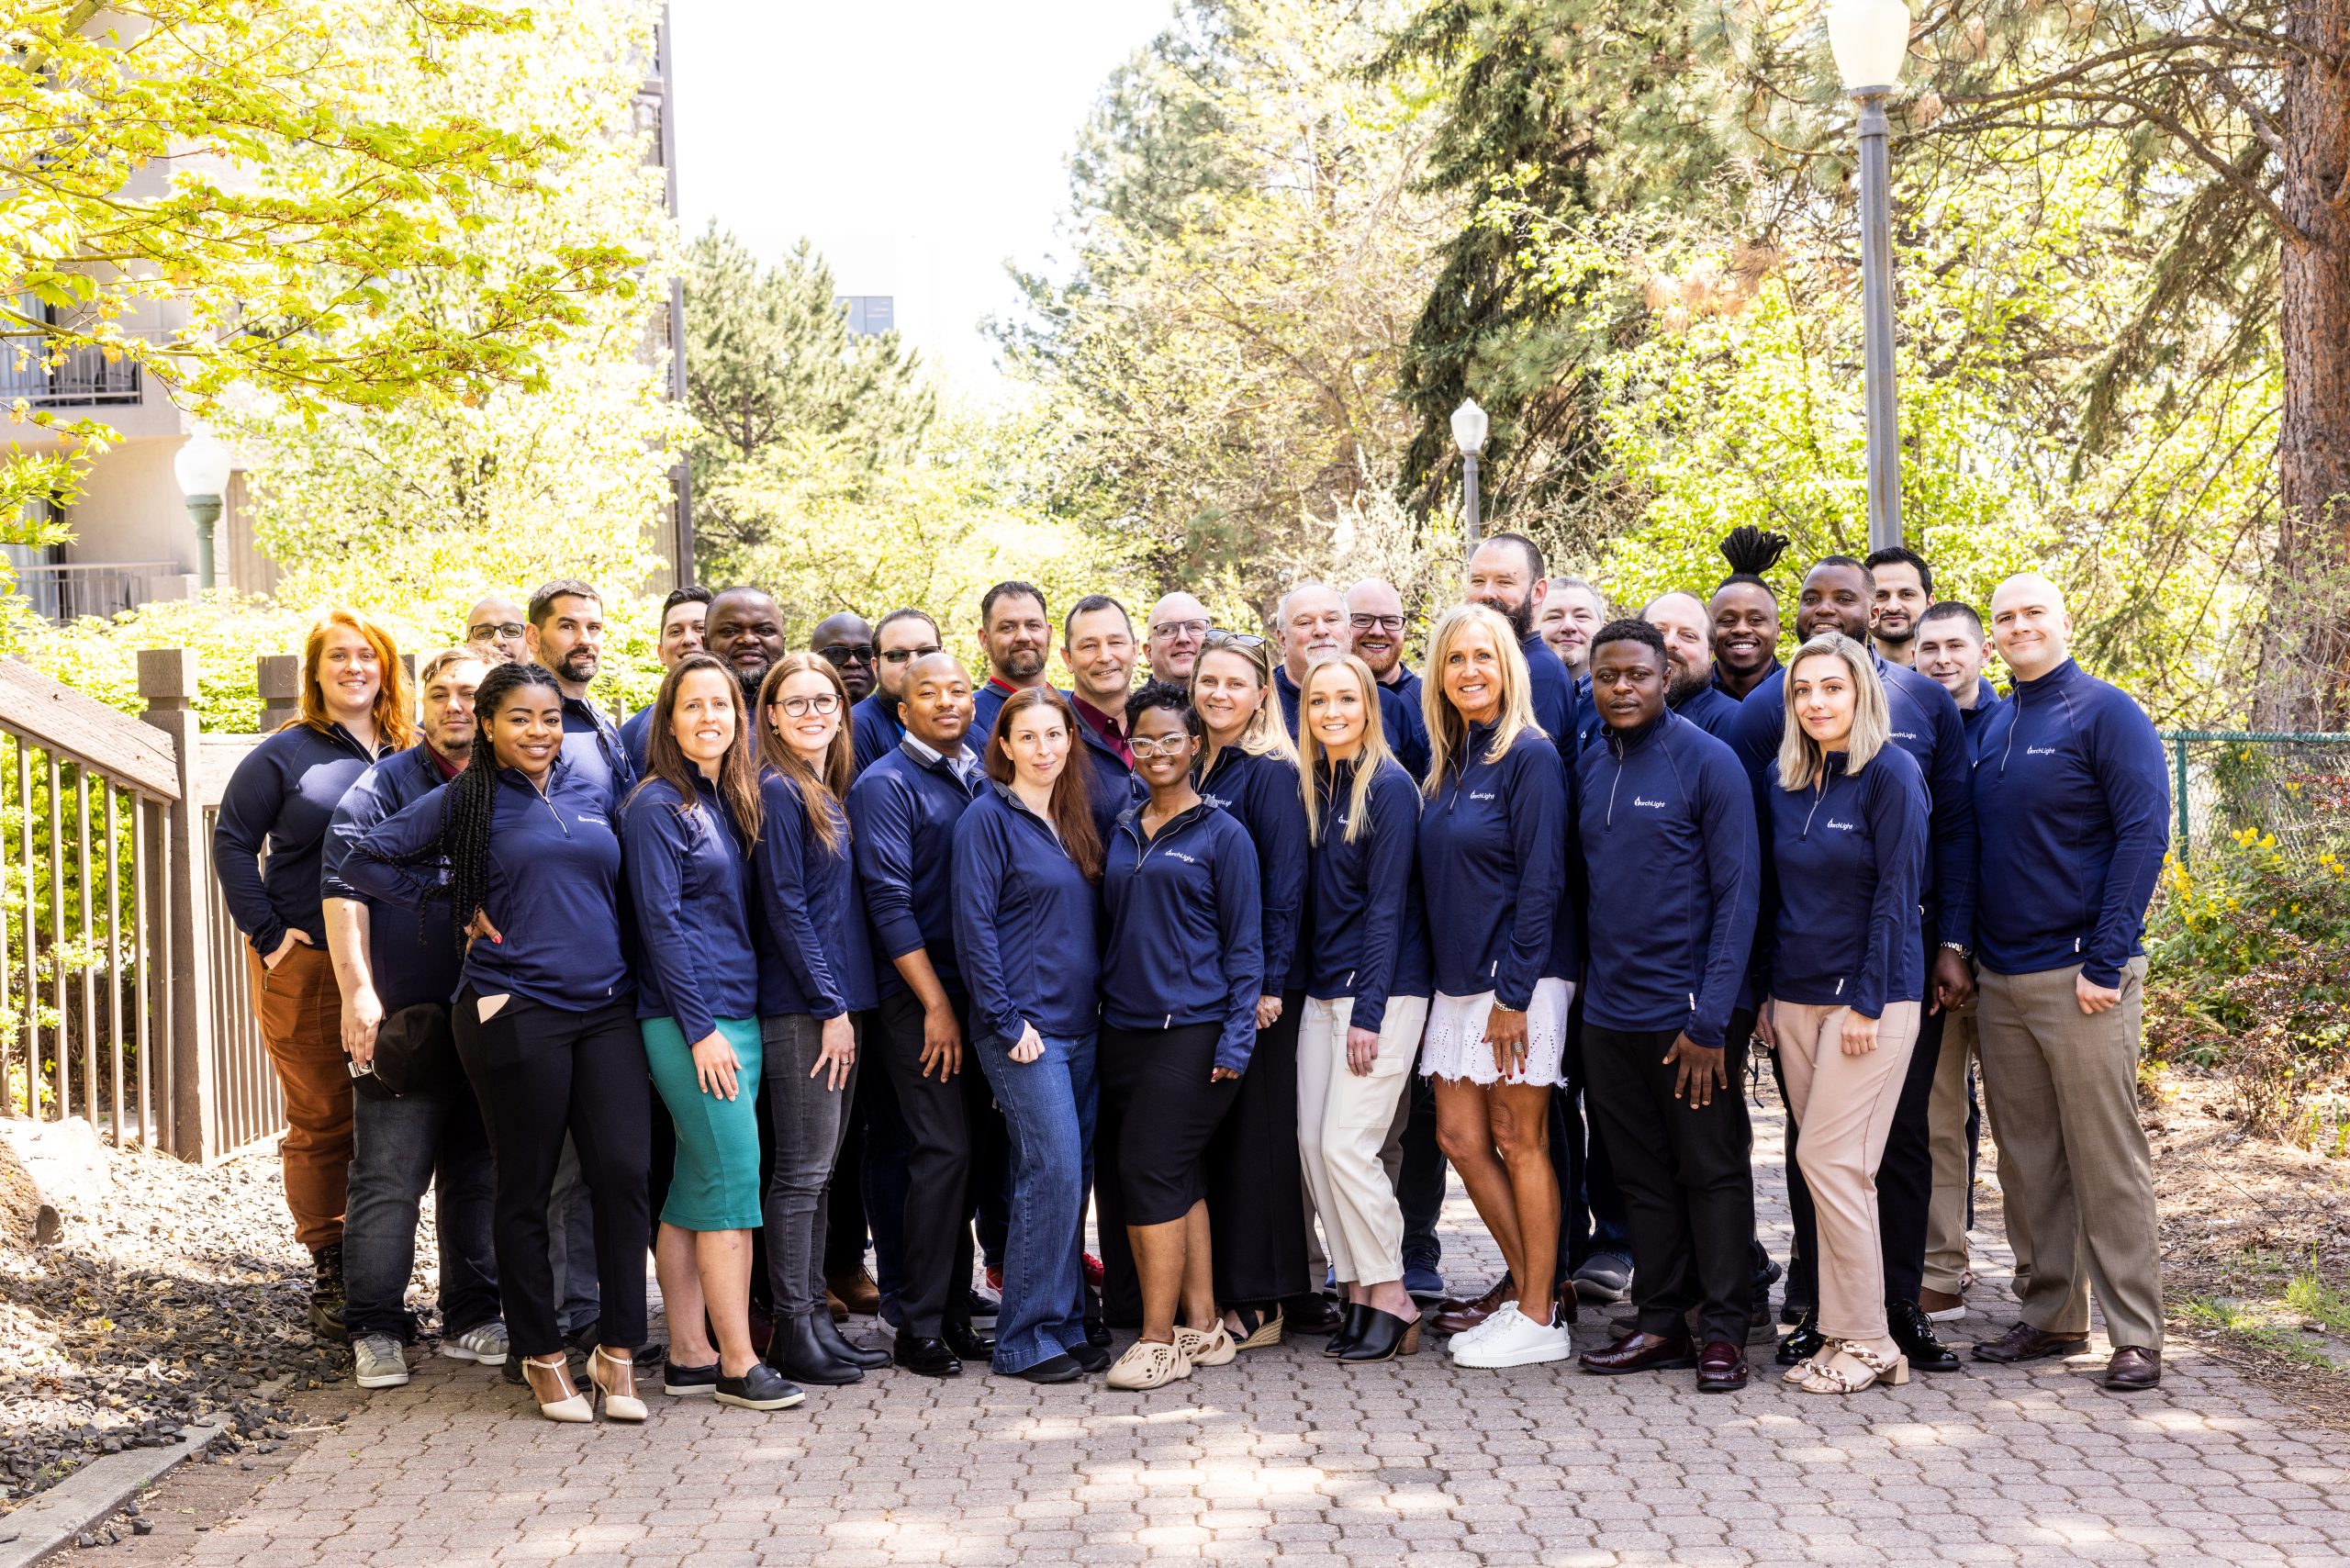
Bring Us the Situation. We’ll Help Define the Right Level of Leadership.
You do not need to arrive knowing whether you need eight hours a month, forty hours a month, a vCISO, a vCIO, or both. Start with what leadership is trying to solve. We can help determine what level of involvement makes sense and what the first priorities should be.
Clarify the Leadership Gap
Is the real problem cybersecurity leadership, technology strategy, board communication, compliance pressure, vendor ownership, budgeting, or a combination of several?
Define the Right Depth
The engagement can range from recurring executive guidance to active program ownership. The right starting point depends on the work, not a predetermined package.
Turn It Into a Working Plan
Roadmaps, budgets, owners, KPIs, evidence, board reporting, and regulatory preparation should connect to one practical operating plan.
Start With the Situation.
Maybe an examination is approaching. Maybe the board wants better visibility. Maybe a technology roadmap has stalled, vendors are pulling in different directions, or the organization simply needs experienced leadership without adding another full-time executive role.
You do not need to translate that into a service package before talking with us. Tell us what is happening, what leadership is trying to accomplish, and where the organization feels exposed.
Talk With TorchLight.
Give us a little context about what your leadership team is trying to solve. We’ll connect you with the right person and help determine the best next step.