Secure Public Services. Clear Accountability.
Technology supports everything from public safety and finance to records, communication, permitting, and everyday constituent services. TorchLight brings managed IT, cybersecurity, resilience, and governance together so public-sector organizations can operate with confidence.
Public-Sector IT Has More to Answer For.
Government IT services have to support more than technology. They have to support the public services, people, records, decisions, and operations that depend on that technology every day.
A service interruption can affect employees, public safety teams, finance departments, constituent services, and the public itself. That makes reliable managed IT services, tested recovery, patching, infrastructure management, and responsive support part of a broader continuity responsibility.
At the same time, identities, endpoints, email, cloud platforms, and sensitive information require active protection. TorchLight connects day-to-day IT with managed security services so public-sector cybersecurity does not become a separate collection of tools, alerts, and vendors with unclear ownership.
Governance matters too. Policies, technical controls, documentation, vendor responsibilities, and evidence need to hold together when leadership, auditors, regulators, insurers, or other stakeholders ask how risk is being managed. Our cybersecurity audit and compliance services help turn those expectations into practical controls, evidence, remediation, and ongoing accountability.
Government cybersecurity works better when operations, security, compliance, and ownership are managed as one environment instead of four separate problems.
Continuity
Public services depend on systems being available. Monitoring, patching, backups, recovery planning, and responsive support help keep everyday operations moving.
Security
Endpoints, identities, email, cloud services, and infrastructure need continuous visibility so suspicious activity can be investigated and acted on before it becomes a larger incident.
Accountability
Internal teams, outside vendors, cloud providers, and technology partners all touch the environment. Clear responsibility keeps important work from disappearing between organizations.
Evidence
Policies and controls need documentation behind them. Useful evidence shows what is operating, who owns it, what was found, and how identified risk is being addressed.
Public-Sector IT Rarely Answers to One Rulebook.
Government cybersecurity requirements can change with the agency, jurisdiction, information being handled, systems in use, cloud architecture, contracts, and services being delivered.
Our goal is to understand which requirements actually matter, translate them into operating controls, and maintain evidence that those controls are working. TorchLight’s cybersecurity audit, assessment, and compliance services help public-sector organizations connect those expectations to the technology environment itself.
Not every law, policy, program, or framework below applies to every government entity. Scope can depend on the organization, data, funding, contracts, cloud use, jurisdiction, and services involved. Legal or regulatory applicability should be confirmed with the appropriate counsel, regulator, agency authority, or governing body.
FISMA & NIST Risk Management Framework
FISMA requires federal agencies to maintain agency-wide information security programs. NIST’s Risk Management Framework provides the repeatable risk-based process used to categorize systems, select and implement controls, assess effectiveness, authorize operation, and continuously monitor risk.
NIST SP 800-53
NIST SP 800-53 provides a broad catalog of security and privacy controls covering areas such as access control, configuration management, incident response, authentication, contingency planning, system integrity, monitoring, and supply-chain risk.
CJIS Security Policy
The FBI CJIS Security Policy establishes security requirements for protecting Criminal Justice Information and the systems, users, devices, networks, and service providers that access or support it. The current published policy is Version 6.1, dated June 25, 2026.
IRS Publication 1075 & IRC §6103
Government organizations receiving Federal Tax Information must protect that information against unauthorized access, disclosure, loss, or misuse. IRS Publication 1075 translates federal safeguarding requirements into security, reporting, operational, and contractor expectations.
HIPAA Security Rule
The HIPAA Security Rule establishes administrative, physical, and technical safeguards for electronic protected health information. Government entities are subject to it when they operate as covered entities or business associates within HIPAA’s scope.
FedRAMP
FedRAMP provides a standardized, reusable approach to security assessment and authorization for cloud computing products and services used within federal agency systems. Whether a particular cloud use falls within FedRAMP scope depends on the federal agency use case.
GovRAMP
Formerly StateRAMP, GovRAMP supports standardized security requirements and independent verification for cloud and technology providers serving government. It is an assurance program, not a universal federal or state cybersecurity law.
NIST Cybersecurity Framework 2.0
NIST CSF 2.0 gives government and private organizations a common structure for understanding and managing cybersecurity risk across Govern, Identify, Protect, Detect, Respond, and Recover outcomes. The framework itself is not a universal government mandate.
Requirements Only Matter When They Become Operating Controls.
TorchLight helps connect regulatory and framework expectations to technical implementation, risk assessment, evidence, remediation, security operations, and accountable technology leadership.
Government IT & Cybersecurity, Managed as One Environment
Technology operations, cybersecurity, Microsoft 365, recovery, compliance support, vendors, and strategic leadership should reinforce one another. TorchLight brings those disciplines together under clear accountability.
Explore Managed IT ServicesHow We Work
TorchLight can operate as the primary technology partner or work alongside internal government IT teams through a co-managed model that adds security, depth, tooling, and specialized expertise without replacing the people already responsible for the environment.
Explore Co-Managed IT & SecuritySecurity, Risk & Leadership
Managed security, assessments, compliance support, incident readiness, and fractional vCISO or vCIO leadership help connect technical controls to risk, policy, budgets, priorities, and public-sector accountability.
Explore vCISO & vCIO ConsultingA Clearer View of What Sits Behind Public-Sector IT.
The help desk is only the visible edge of the environment. The real work extends into infrastructure, identities, cybersecurity, cloud services, recovery, vendors, evidence, and the decisions that determine what happens next.
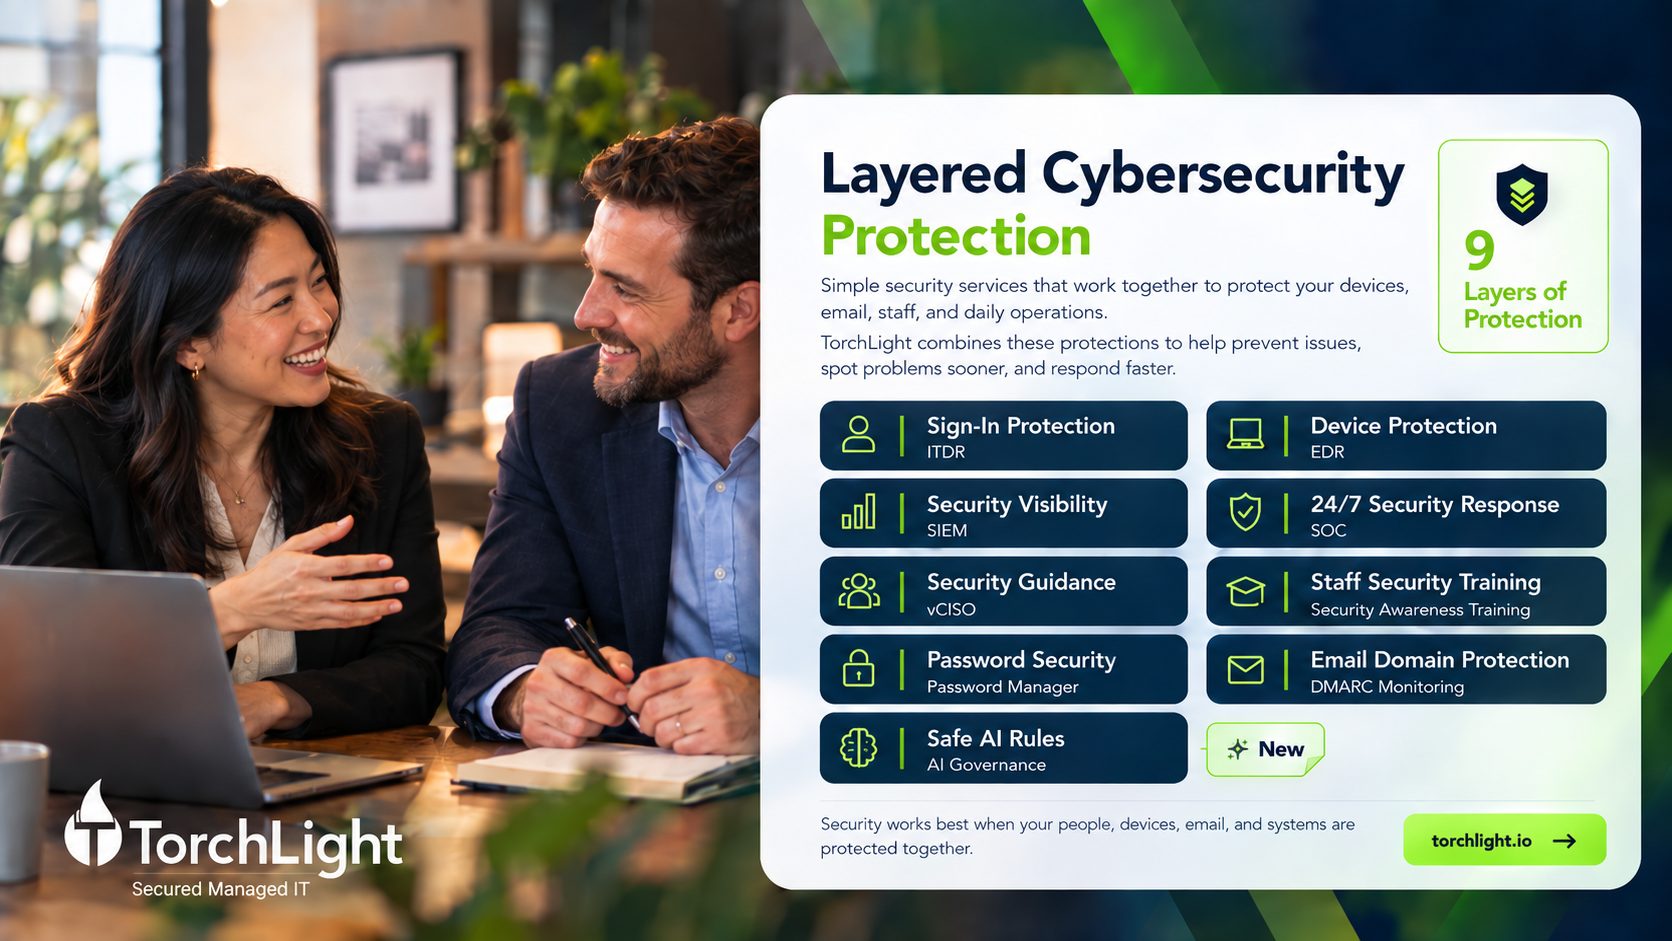
TorchLight’s managed security services connect continuous monitoring, endpoint protection, identity security, email security, investigation, and response to the same environment being supported day to day.
Our audit, assessment, and compliance services add another layer: understanding requirements, validating controls, identifying gaps, organizing evidence, and building remediation plans that can survive scrutiny.
That gives government leaders a more complete operating picture. Instead of separate conversations about IT support, cybersecurity, compliance, and strategy, the organization can make decisions from one view of the environment.
Public-sector IT is stronger when support, security, compliance, and leadership operate as one accountable system.
Built for Environments Where Tech Gets Examined.
Public-sector leaders need to understand how their environment is secured, who is accountable, what evidence exists, and what happens when something fails.
TorchLight’s approach was shaped inside regulated organizations where technology decisions are examined by auditors, regulators, executives, boards, and the people those organizations serve.
That experience extends into public-sector security leadership. TorchLight executive consulting experience includes CISO and vCISO-style leadership in large public-sector and higher-education environments, alongside deep backgrounds in security architecture, incident response, penetration testing, and enterprise cybersecurity.
The result is a government IT and cybersecurity model focused on more than implementation. Controls need owners. Findings need remediation. Risks need decisions. And leadership needs a clear view of what is actually happening inside the environment.
Strong public-sector cybersecurity is not simply about meeting a requirement. It is about building an environment that can explain and defend how risk is being managed.
Built Around Regulated Environments
TorchLight’s operating model grew inside organizations where cybersecurity, compliance, resilience, documentation, and stakeholder trust carry real consequences.
Executive Security Leadership Experience
TorchLight leadership experience includes CISO and vCISO-style responsibilities in large public-sector and higher-education environments.
Controls That Can Be Explained
Assessments, documentation, remediation, testing, and ongoing governance help turn cybersecurity expectations into operating practices leadership can understand and defend.
Government Intelligence.
Cybersecurity guidance is more useful when it connects emerging threats and real incidents to the decisions public-sector technology leaders have to make.
These TorchLight briefings focus on current public-sector cybersecurity issues, operational resilience, Microsoft security, identity risk, and vulnerabilities that can affect government and other regulated environments.
What happened matters. What your agency should examine, validate, patch, test, or prepare for next matters more.
Spokane Public Schools Cybersecurity Incident: What We Know So Far
A developing local cybersecurity incident shows how quickly technology disruption can become an operational issue involving payroll, communications, leadership, recovery, and the people a public organization serves.
Read the Latest Update
How the SharePoint Chain Broke on July 14, 2026
Four SharePoint vulnerabilities were chained in active attacks while CISA imposed rapid remediation requirements on federal agencies. The incident is a useful case study in patching, unsupported systems, exposure, and response readiness.
Read the Threat Analysis
Why Device Logins Just Became a Liability
Device-code phishing can turn a legitimate Microsoft authentication flow into unauthorized access without stealing a password. The 2026 campaign reached government and other regulated organizations, putting identity configuration and monitoring in the spotlight.
Read the Identity BriefingPublic-Sector IT Should Come With Proof.
Government technology has to work in the real world, withstand scrutiny, and keep responsibility clear when something needs attention.
Experience in Regulated Environments
TorchLight was built around organizations where cybersecurity, compliance, resilience, documentation, and stakeholder trust all carry real consequences.
Security Does Not Keep Office Hours
Public-sector systems, identities, endpoints, and security events can require attention long after employees leave the office.
IT, Security & Strategy Together
Managed IT, cybersecurity, compliance support, Microsoft 365, vendors, and strategic leadership work better when accountability does not disappear between providers.
Let’s Make Government IT Easier to Trust.
You do not need to have the solution mapped out before starting the conversation.
Maybe the challenge is aging infrastructure, cybersecurity exposure, Microsoft 365, compliance requirements, staffing limitations, vendor accountability, recovery readiness, or simply not having a clear enough picture of the environment. Tell us what needs to improve and we’ll start there.
Start the Conversation
Give us a little context about your government IT, cybersecurity, compliance, or technology environment and we’ll connect you with the right person at TorchLight.