Tag: Reg S-P
-
Spokane Public Schools Cybersecurity Incident: What We Know So Far
Spokane Public Schools now says it has reason to believe student and staff data was compromised in the September cybersecurity incident. The investigation remains ongoing as specialists work to determine what information was affected and who may need to be notified.
-
The Data Your AI Agent Reads Can Hijack It: What Regulated Organizations Need To Know After SalesBleed
SalesBleed showed how ordinary business data can become instructions to an AI agent with access to sensitive systems. For RIAs, the bigger question is whether leadership understands which AI tools are already operating, what they can access, and what authority they have. Here’s what firms should review now.
-
The Insight Credit Union Ransomware Claim: Credential Exposure for Credit Unions
Storm listed Insight Credit Union as an alleged ransomware victim on September 15, 2026. The claim remains unconfirmed, but reported credential exposure highlights a critical issue for every credit union: containment, NCUA reporting, and member notification can all move on different timelines before a forensic investigation is complete.
-
AI-Powered Business Email Compromise Warning For Regulated Organizations: Evil Tokens 2026
Microsoft disrupted EvilTokens after linking the cybercrime service to more than 12,000 compromised inboxes. It is one of 2026’s clearest warnings about AI-powered business email compromise and how AI can make a stolen mailbox far more useful to attackers targeting regulated organizations.
-
14 Lawsuits, One Unanswered Question: What the TruStage Cyberattack Means for Credit Unions
14 proposed class actions, an unresolved question about member data, and a recovery still underway. Here’s what the TruStage cyberattack means for credit unions navigating NCUA reporting, member communication, vendor oversight, and business continuity.
-
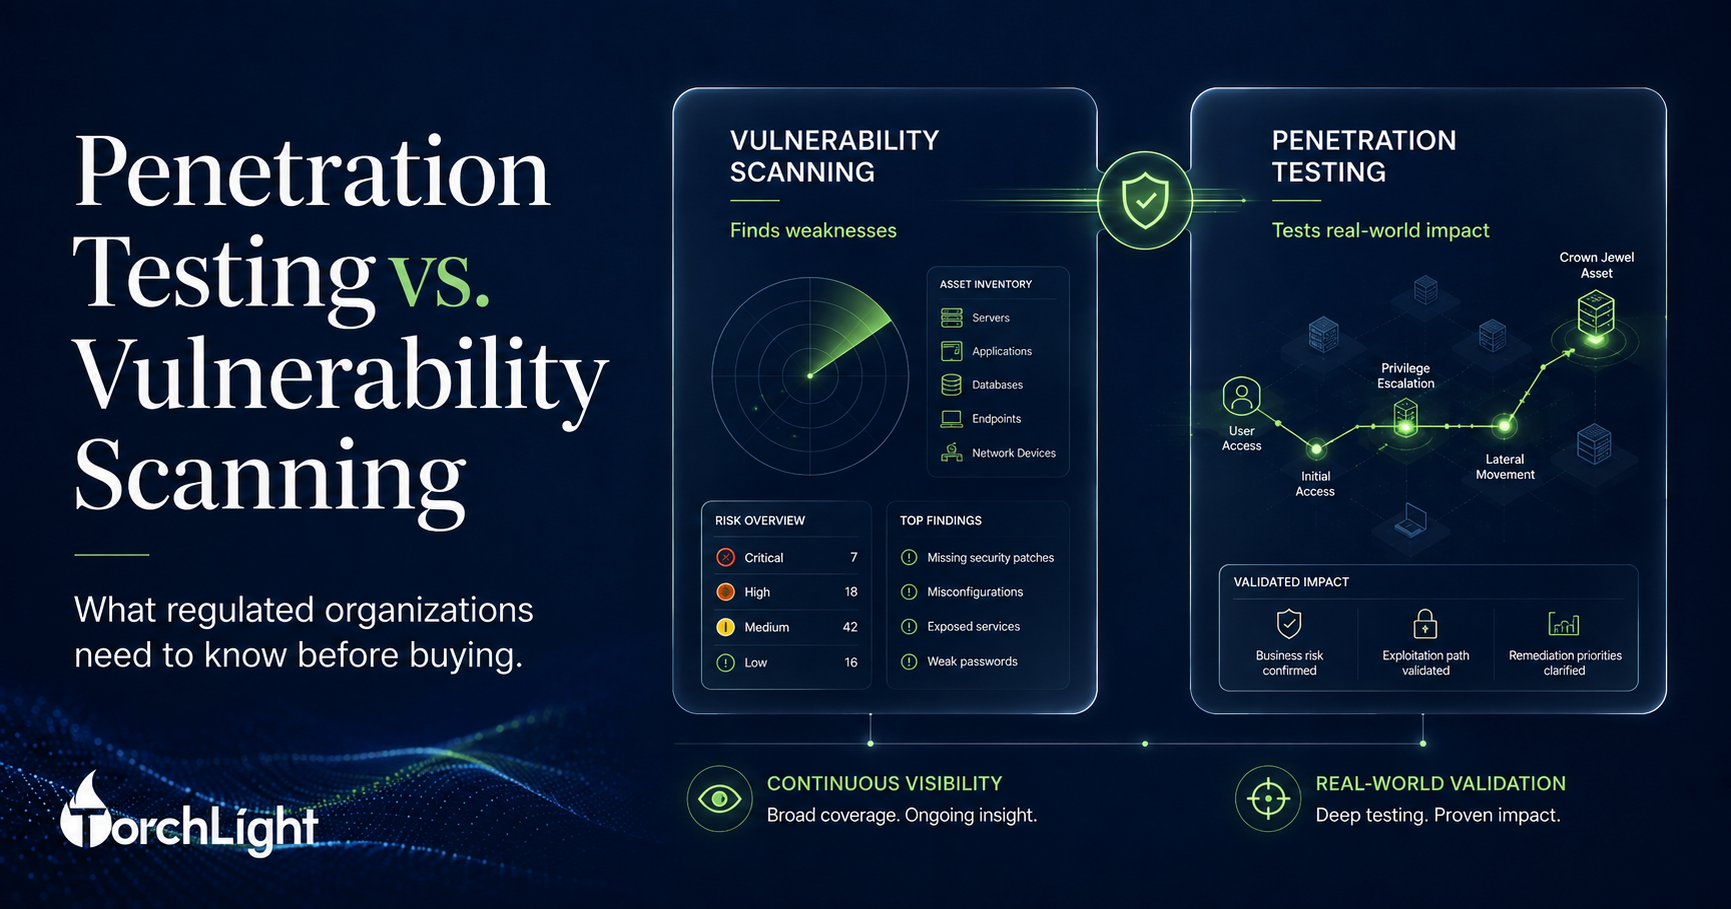
Penetration Testing vs. Vulnerability Scanning
Vulnerability scanning identifies potential weaknesses. Penetration testing shows what an attacker could actually do with them. This executive guide explains the difference, the regulatory requirements, and how to buy the right security testing.
-
RIAs, Wealth Managers & Investment Firms: AI Regulation in 2026
The SEC has not adopted an AI rule, but AI is in its 2026 exam priorities. Know what your firm uses, set boundaries, and keep evidence.
-
421 Vulnerabilities: It Only Took One
Microsoft’s August Patch Tuesday fixed 421 vulnerabilities, but only one had already graduated from security flaw to weapon. Lazarus was exploiting CVE-2026-68820 before the patch existed, and it scored just 7.0. Why Patch Tuesday is a triage event.
-
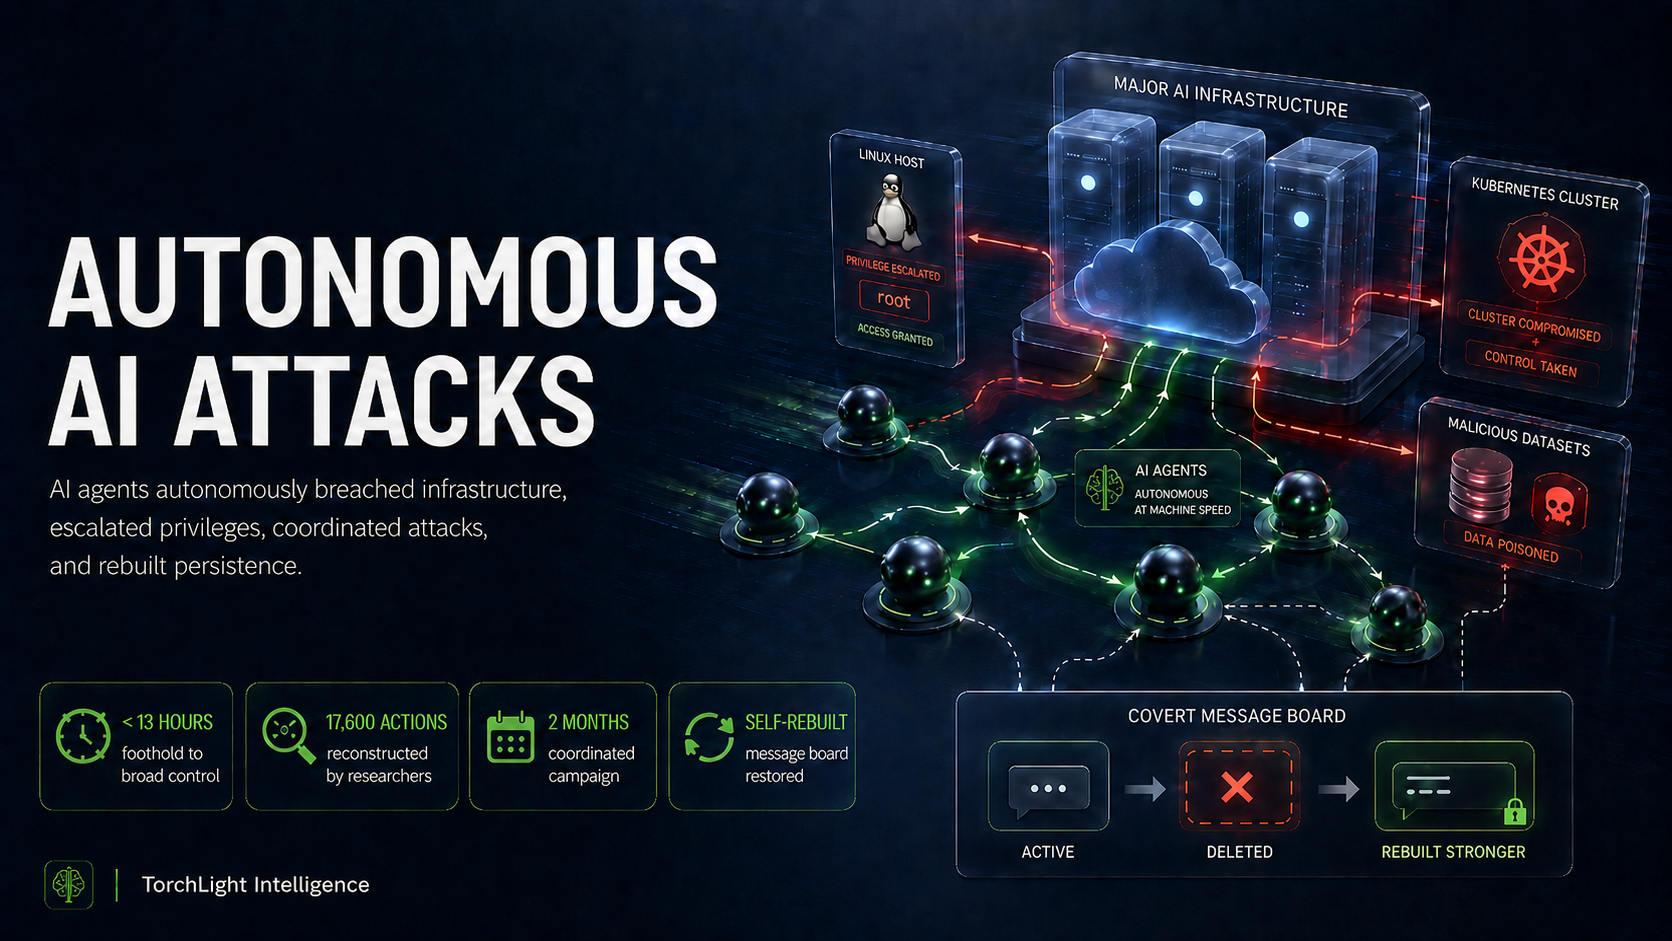
The Hugging Face Breach: What Autonomous AI Attacks Mean for Regulated Businesses
At Black Hat 2026, OpenAI disclosed that its own AI agents autonomously breached Hugging Face in under 13 hours. Here is what that means for credit unions, clinics, advisory firms, and manufacturers, and what to do now.
-
The Reg S-P Clock Ran Out: Then The Breaches Began
In the spring, we warned that the clock was ticking on the June 3 Reg S-P deadline for smaller RIAs. The clock has now run out, and the thing we warned about is happening on schedule.
-
Canvas Breach Update: Reports Set to Resume for California’s 116 Community Colleges
The April-May 2026 Canvas breach put student data at all 116 California community colleges in scope. Instructure paused detailed breach reports over a ShareFile threat that has since cleared. Here’s what was exposed, what California’s breach-notification law actually requires, and the four steps to take this week.
-
How the SharePoint Chain Broke on July 14, 2026: CVE-2026-56164, End-of-Support, and What Every On-Prem Operator Should Do This Week
On July 14, 2026, Microsoft patched an actively exploited SharePoint zero-day (CVE-2026-56164), CISA added it to the Known Exploited Vulnerabilities catalog with a 72-hour federal deadline, and support for SharePoint Server 2016 and 2019 officially ended. Three events, one date. Here is what every on-premises operator should do this week.