Managed IT & Cybersecurity for Credit Unions
TorchLight combines managed IT, 24/7 cybersecurity, compliance support, and technology leadership for credit unions that need reliable member services, stronger security, and fewer surprises during examinations.
Built around the realities of regulated financial institutions, including NCUA Part 748, GLBA safeguards, incident response readiness, third-party risk, and audit evidence.
Credit Union IT Has to Hold Up Under Scrutiny.
A credit union is not evaluated on whether it bought the right collection of security products. Its information security program has to demonstrate that technology risk is identified, managed, monitored, documented, and governed as part of the institution’s normal operations.
The NCUA’s Information Security Examination procedures examine areas such as management’s ability to manage technology risk, the expertise available to the credit union, board-approved policies and procedures, internal controls, and safeguards protecting member information.
That is why TorchLight treats managed IT , cybersecurity, governance, compliance evidence, and executive technology leadership as parts of the same operating environment instead of separate projects.
Examination readiness should be the result of how your credit union operates every day, not a scramble that begins when an examiner asks for evidence.
Examination readiness is an operating state.
A mature information security program connects governance, technical controls, incident response, vendor oversight, and evidence into one defensible system.
Governance & Expertise
Technology risk needs clear ownership, appropriate expertise, documented policies, board visibility, and decisions that can be tied back to the credit union’s actual risk profile.
Safeguard Member Information
Administrative, technical, and physical safeguards must work together to protect member information, identities, endpoints, systems, communications, and the data your institution depends on.
Incident Readiness & Resilience
Detection is only the beginning. Credit unions need defined escalation, containment, communications, recovery, and regulatory reporting procedures when a significant event occurs.
Vendor Oversight & Evidence
Policies are not enough. Your program needs repeatable evidence showing how controls operate, how third-party risk is managed, how findings are remediated, and who owns the next action.
Protect the Entire Credit Union Environment.
Credit union technology does not stop at the help desk or the firewall. Identities, endpoints, cloud applications, branches, vendors, member information, and the systems supporting digital banking all depend on one another.
A compromised identity can become a Microsoft 365 incident. A neglected endpoint can become a security event. A third-party weakness can become an operational problem. And an unresolved IT issue can quickly become a member-service problem.
TorchLight brings IT operations, cybersecurity, remediation, governance, and technology strategy into one accountable operating model so gaps do not disappear between separate providers or internal teams.
Security works better when the same operating model can detect the problem, understand the business impact, assign ownership, and drive the fix through completion.
One environment. One operating model.
IT operations and security controls should reinforce each other across the systems your institution depends on.
Built for Credit Unions. Not Adapted to Them.
Supporting a regulated financial institution requires more than a help desk, security dashboard, or compliance checklist. Technology decisions have to work inside the real operating environment of the credit union.
TorchLight combines long-standing credit-union experience, security and audit expertise, and examination perspective with the team responsible for improving the environment after the ticket, alert, assessment, or finding.
Built for environments where trust matters.
Member service, cybersecurity, regulatory scrutiny, operational resilience, and executive accountability are not separate technology problems.
Ownership Beyond the Ticket
Restoring service matters. So does understanding why the problem happened, whether it will happen again, and what needs to change to prevent the next incident. Recurring problems should become improvement work, not another ticket next month.
Security Tied to Operations
A security finding should not disappear into a report. The people protecting the environment need a direct path to the people who manage the affected identities, endpoints, systems, cloud services, and vendors so remediation actually happens.
Reduce Avoidable IT Cost
Recurring tickets, downtime, technical debt, unnecessary licensing, vendor confusion, security findings, and remediation backlogs consume resources without improving member service.
Our Zero-Cost IT Model Tailored For Credit Unions.
Most managed IT services and cybersecurity services companies rely on reactive support and disconnected tools. Traditional managed IT company models separate IT and security, creating risk and compliance gaps. TorchLight’s Zero-Cost IT approach brings everything together into one unified system that converts stability and security improvements into measurable and reportable cost offsets.
Stability Foundation
Stop downtime, noise, and operational and financial leakage.
Stability Foundation
Standardize the environment, reduce recurring incidents, and eliminate avoidable downtime, noise, and operational leakage. This predictable foundation is what every higher stage depends on.
Security Layer
24/7 proactive protection and hardening.
Security Layer
Add continuous monitoring, hardening, identity protection, endpoint security, patching, and recovery readiness. The goal is proactive protection rather than waiting for incidents to become emergencies.
Compliance Accelerator
Audit-ready evidence and zero-finding confidence.
Compliance Accelerator
Turn working controls into repeatable, audit-ready evidence. Continuous documentation and evidence collection reduce last-minute compliance scrambles and support stronger exam readiness.
Proof Point
Independent validation plus executive advisory.
Proof Point
Independently validate whether the controls actually work through penetration testing and assessments, while executive vCISO/vCIO guidance helps leadership prioritize technology, risk, and investment.
Competitive Peak
IT becomes a strategic advantage, not a cost center.
Competitive Peak
Once stability, security, compliance, and proof are established, technology can support growth, automation, resilience, and better business decisions.
Practical Guidance for Credit Union Leaders.
Go deeper on the operational, cybersecurity, and examination-readiness issues that matter to regulated financial institutions.
Risk Aligned. Reward Defined.
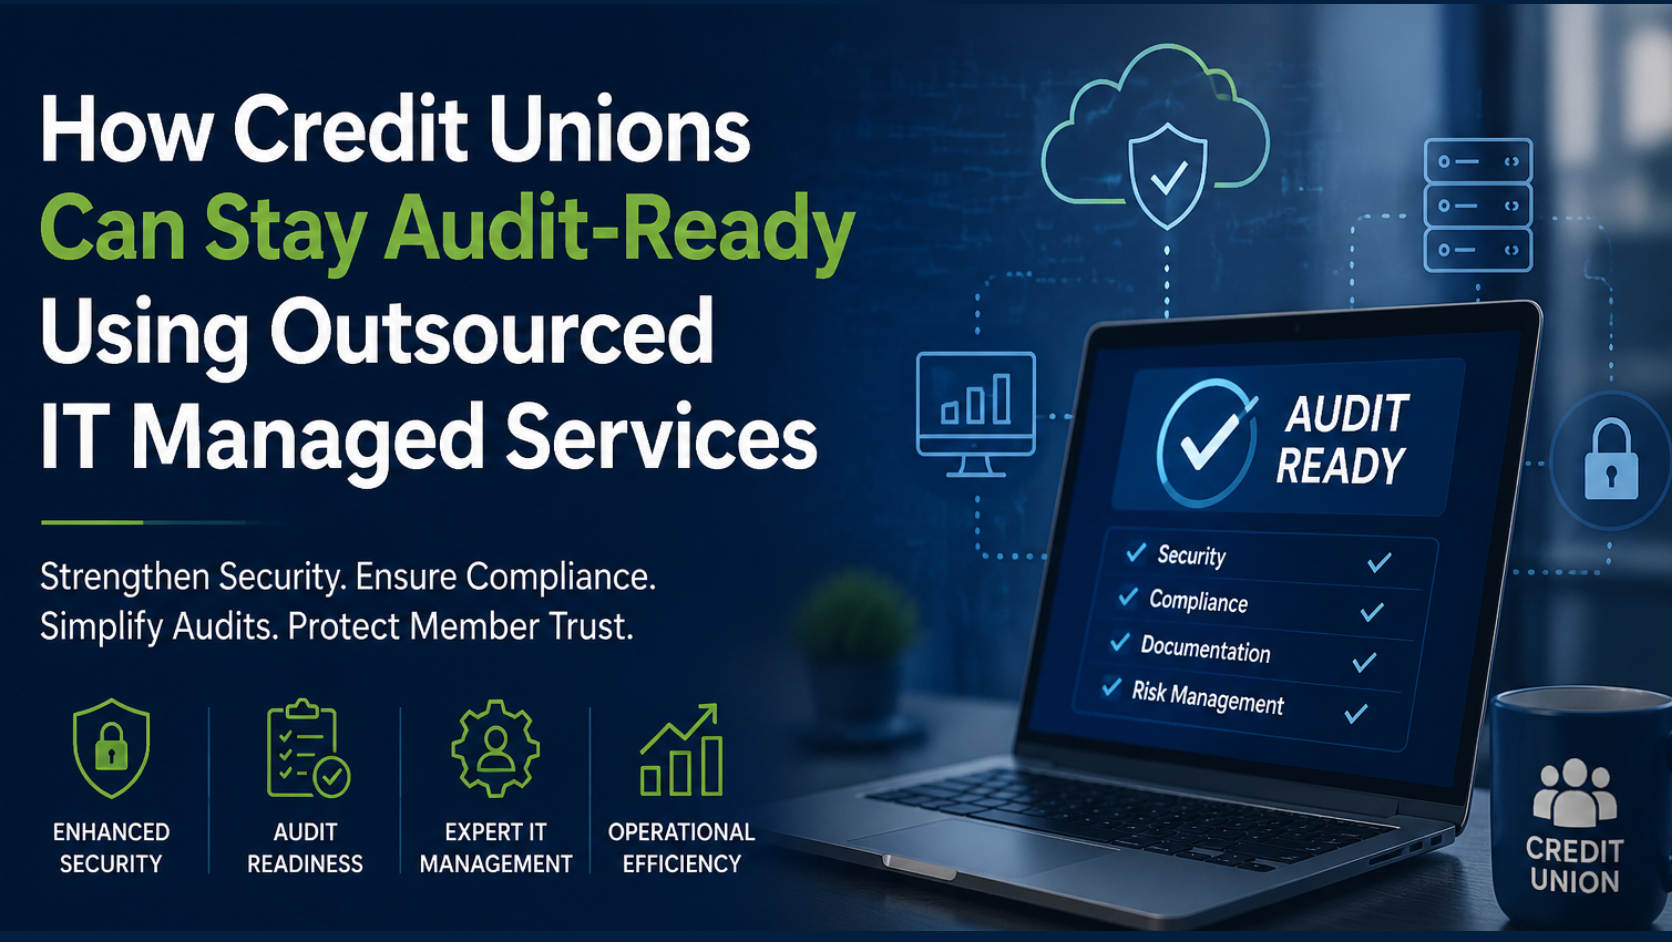
How Credit Unions Can Stay Audit-Ready Using Outsourced IT Managed Services
Why examination readiness works better as a continuous operating discipline than a documentation scramble before the next review.
Read the Article
Vendor Risk Management for Credit Unions: What the NCUA Expects
A practical look at vendor due diligence, ongoing monitoring, critical-provider oversight, and the documentation behind third-party risk management.
Read the Article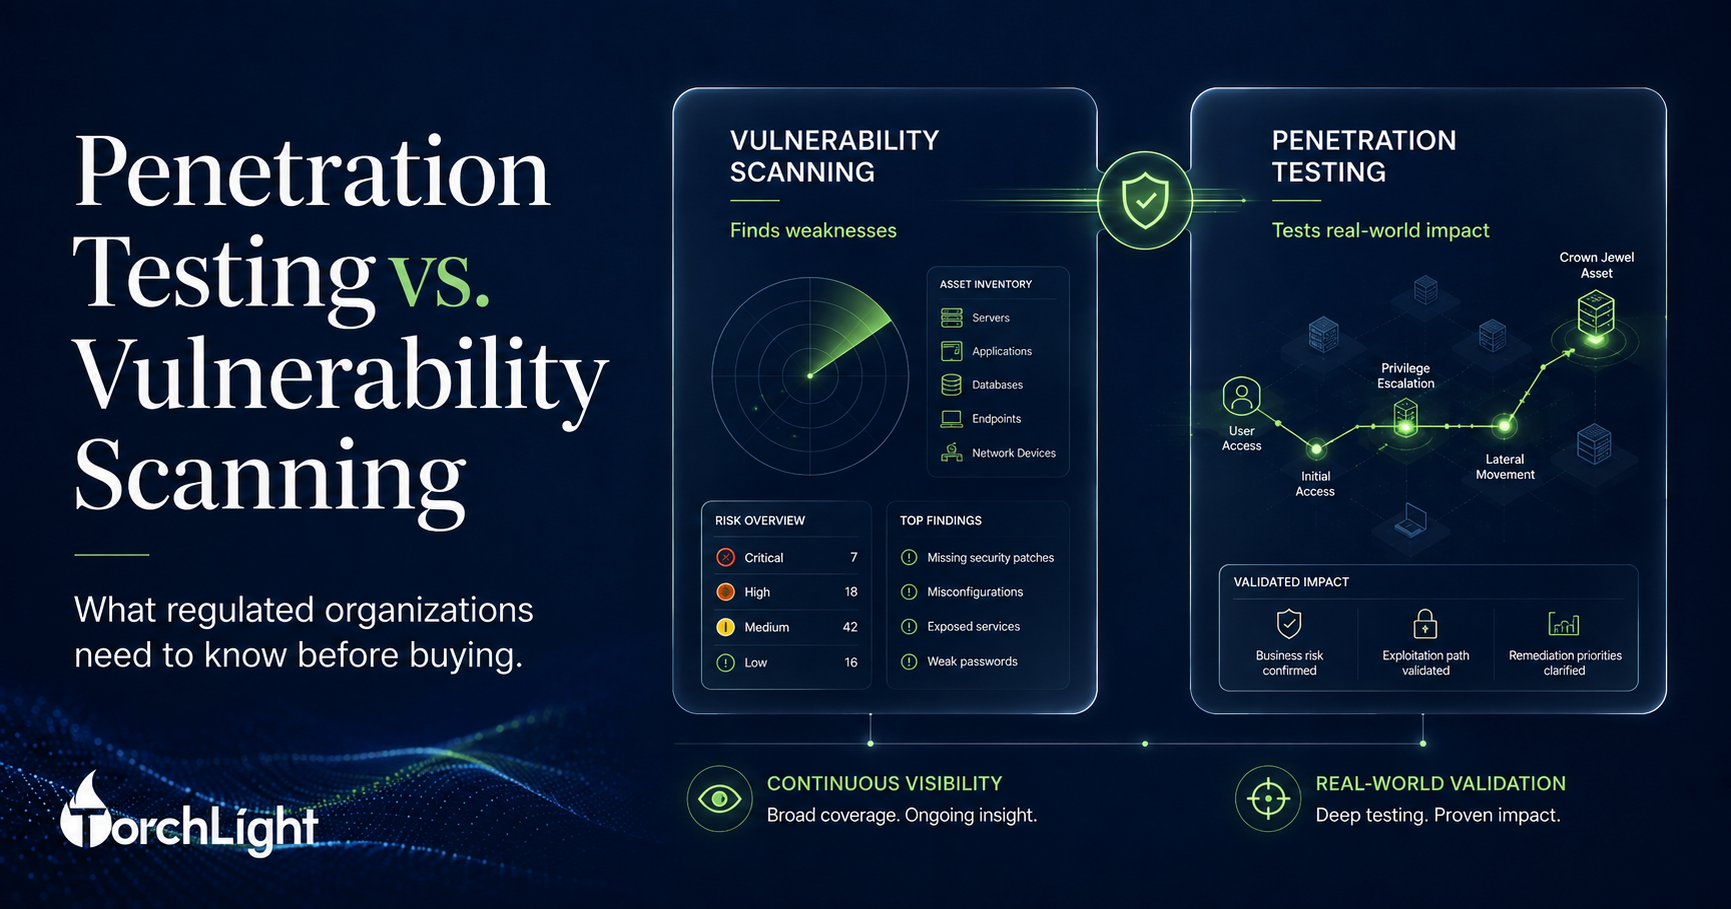
Penetration Testing vs. Vulnerability Scanning
Understand what each type of testing proves, how they differ, and what regulated organizations should know before purchasing either one.
Read the ArticleWhy Clients Continue to Choose TorchLight.
Credit unions do not need more technology noise. They need a partner that can make security part of everyday IT, translate complexity into clear decisions, own problems through remediation, and build relationships that hold up over time.
Explore Why TorchLightSecurity Is the Starting Point.
For a credit union, security cannot be added after the environment is built. Identity, endpoints, Microsoft 365, infrastructure, vendors, recovery, and everyday IT decisions all influence the institution’s risk.
Clarity Before Complexity.
Boards and executives should understand what happened, what risk remains, what needs to happen next, and why. Technical expertise should make leadership more confident, not more dependent on technical language.
Somebody Owns the Outcome.
A finding, ticket, vendor problem, or security event should not disappear between teams. TorchLight is built around clear accountability, follow-through, and fewer opportunities for responsibility to fall between the cracks.
Built for the Long Term.
The goal is not dependence on TorchLight. It is a relationship where useful guidance, transparent decisions, clear expectations, and consistent follow-through build trust over years rather than individual projects.
Sometimes the best proof is the relationship itself.
PrimeSource Credit Union first engaged TorchLight for a security assessment and gap analysis in 2007. That work developed into a long-term strategic technology and cybersecurity relationship.
Evidence Matters. So Do Outcomes.
A technology partner serving a regulated institution should be able to point to more than tools, certifications, and promises.
Client Rating
A near-perfect satisfaction score built through responsive service, accountability, and long-term client relationships.
Regulatory Exam Pass Rate
A 100% exam pass rate for TorchLight clients operating at or above Stage 3 of our maturity model.
Regulated IndustriesYears Serving Regulated Organizations
Experience supporting environments where technology, cybersecurity, compliance, resilience, and proof all matter.
Start With the Credit Union You Have Today.
You do not need to have the problem perfectly defined before talking with us. Tell us what is happening, where you are trying to improve, or what your leadership team needs more confidence in. We can start there.
Start the Conversation.
Give us a little context and we will connect you with the right person at TorchLight.