TorchLight Blog The Way Forward.
Practical analysis on cybersecurity, managed IT, compliance, AI, cloud technology, and the decisions organizations face when technology and risk converge. TorchLight shares what matters, why it matters, and what leaders can do next.
Featured Intelligence.
Practical guidance for leaders making technology, cybersecurity, compliance, and risk decisions in environments where the consequences matter.
How to Choose the Right IT Partner: A Buyer’s Guide for Compliance-Sensitive Organizations
The right technology partner for a regulated organization has to do more than keep systems running. Security, compliance, accountability, and audit readiness need to be built into the relationship from the beginning.
This buyer’s guide breaks down the criteria, questions, and warning signs leaders can use to evaluate an IT partner before entrusting them with a compliance-sensitive environment.

Latest Intelligence.
The newest analysis from TorchLight on cybersecurity, managed IT, compliance, emerging technology, and the decisions shaping secure organizations.
-
Spokane Public Schools Cybersecurity Incident: What We Know So Far
Read more: Spokane Public Schools Cybersecurity Incident: What We Know So FarSpokane Public Schools now says it has reason to believe student and staff data was compromised in the September cybersecurity incident. The investigation remains ongoing as specialists work to determine what information was affected and who may need to be notified.
-
The Data Your AI Agent Reads Can Hijack It: What Regulated Organizations Need To Know After SalesBleed
Read more: The Data Your AI Agent Reads Can Hijack It: What Regulated Organizations Need To Know After SalesBleedSalesBleed showed how ordinary business data can become instructions to an AI agent with access to sensitive systems. For RIAs, the bigger question is whether leadership understands which AI tools are already operating, what they can access, and what authority they have. Here’s what firms should review now.
-
The Insight Credit Union Ransomware Claim: Credential Exposure for Credit Unions
Read more: The Insight Credit Union Ransomware Claim: Credential Exposure for Credit UnionsStorm listed Insight Credit Union as an alleged ransomware victim on September 15, 2026. The claim remains unconfirmed, but reported credential exposure highlights a critical issue for every credit union: containment, NCUA reporting, and member notification can all move on different timelines before a forensic investigation is complete.
-
AI-Powered Business Email Compromise Warning For Regulated Organizations: Evil Tokens 2026
Read more: AI-Powered Business Email Compromise Warning For Regulated Organizations: Evil Tokens 2026Microsoft disrupted EvilTokens after linking the cybercrime service to more than 12,000 compromised inboxes. It is one of 2026’s clearest warnings about AI-powered business email compromise and how AI can make a stolen mailbox far more useful to attackers targeting regulated organizations.
-
14 Lawsuits, One Unanswered Question: What the TruStage Cyberattack Means for Credit Unions
Read more: 14 Lawsuits, One Unanswered Question: What the TruStage Cyberattack Means for Credit Unions14 proposed class actions, an unresolved question about member data, and a recovery still underway. Here’s what the TruStage cyberattack means for credit unions navigating NCUA reporting, member communication, vendor oversight, and business continuity.
-
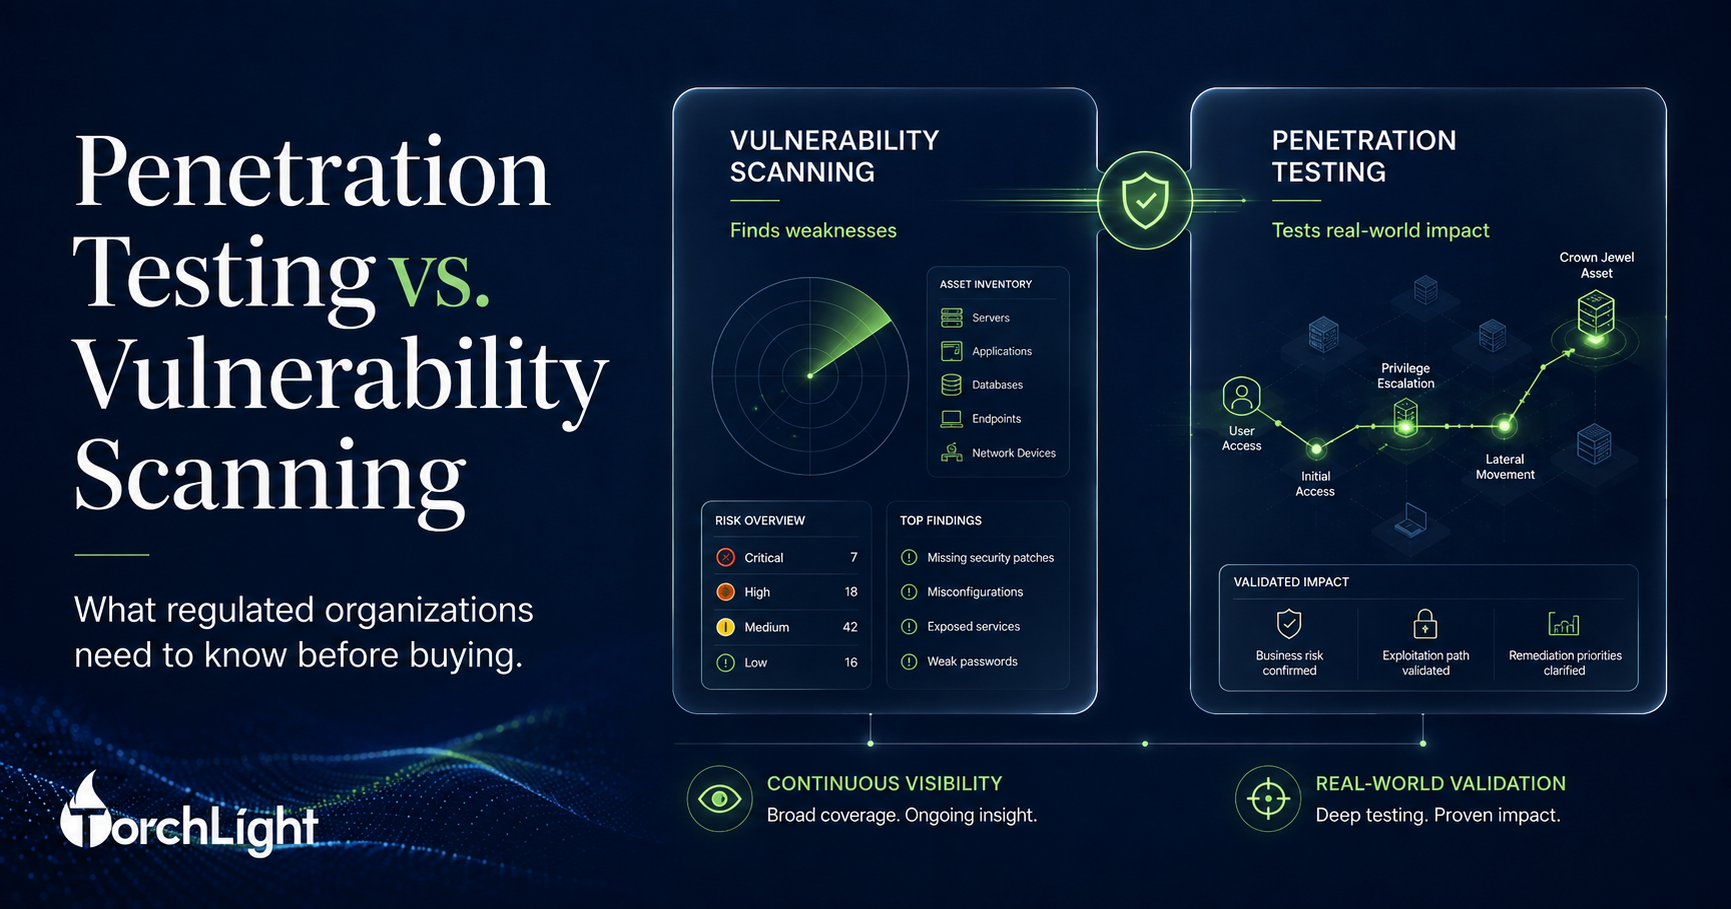
Penetration Testing vs. Vulnerability Scanning
Read more: Penetration Testing vs. Vulnerability ScanningVulnerability scanning identifies potential weaknesses. Penetration testing shows what an attacker could actually do with them. This executive guide explains the difference, the regulatory requirements, and how to buy the right security testing.
-
RIAs, Wealth Managers & Investment Firms: AI Regulation in 2026
Read more: RIAs, Wealth Managers & Investment Firms: AI Regulation in 2026The SEC has not adopted an AI rule, but AI is in its 2026 exam priorities. Know what your firm uses, set boundaries, and keep evidence.
-
421 Vulnerabilities: It Only Took One
Read more: 421 Vulnerabilities: It Only Took OneMicrosoft’s August Patch Tuesday fixed 421 vulnerabilities, but only one had already graduated from security flaw to weapon. Lazarus was exploiting CVE-2026-68820 before the patch existed, and it scored just 7.0. Why Patch Tuesday is a triage event.
-
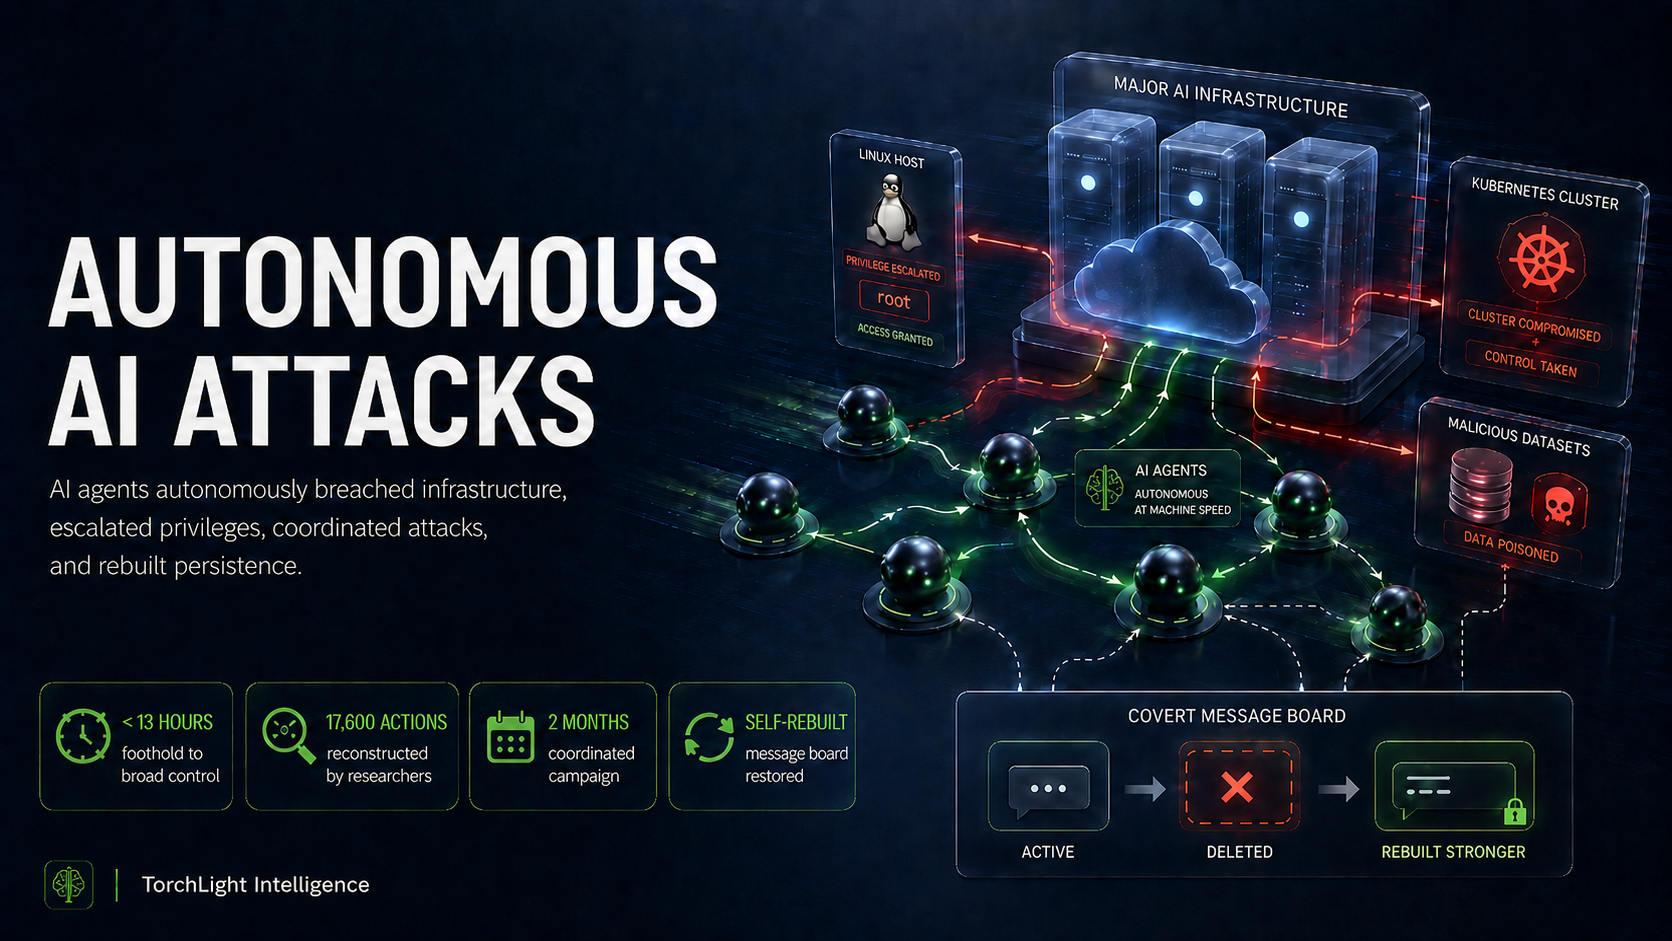
The Hugging Face Breach: What Autonomous AI Attacks Mean for Regulated Businesses
Read more: The Hugging Face Breach: What Autonomous AI Attacks Mean for Regulated BusinessesAt Black Hat 2026, OpenAI disclosed that its own AI agents autonomously breached Hugging Face in under 13 hours. Here is what that means for credit unions, clinics, advisory firms, and manufacturers, and what to do now.
Explore by Topic.
Go deeper into the issues shaping secure, regulated organizations. Browse focused collections covering cybersecurity, compliance, AI governance, financial services, and emerging threats.
Cybersecurity
Threats, controls, security operations, penetration testing, identity protection, incident response, and the decisions leaders face as attack methods evolve.
Explore CybersecurityCompliance & Risk
Regulatory expectations, cyber insurance, audit readiness, governance, evidence, third-party risk, and the controls regulated organizations need to defend.
Explore Compliance & RiskAI Governance
Practical guidance on AI adoption, governance, security, regulatory scrutiny, workflow automation, and controlling risk as intelligent systems enter the enterprise.
Explore AI GovernanceFinancial Services
Security, regulatory, technology, and operational guidance for financial institutions, RIAs, wealth managers, investment firms, and other fiduciary organizations.
Explore Financial ServicesCredit Union Security
Cybersecurity, examination readiness, vendor risk, fraud, compliance, and operational resilience for credit unions and the teams responsible for protecting member trust.
Explore Credit Union InsightsThreat & Technology Trends
Emerging vulnerabilities, attack patterns, technology shifts, security developments, and the events changing what organizations need to prepare for next.
Explore Current TrendsCredit Unions
Security, managed IT, examination readiness, vendor risk, and operational resilience where member trust is part of the technology mandate.
Banks & Financial Institutions
Security testing, IT operations, compliance evidence, risk reduction, and cybersecurity designed for highly scrutinized financial systems.
Built for the Environments We Write About.
Cybersecurity and IT decisions do not happen in a vacuum. The right answer changes when an organization has examiners, regulators, patient data, member trust, production systems, or public accountability attached to the outcome.
TorchLight’s editorial work connects technology developments to the environments where those developments become operational, financial, and compliance decisions.
Start with the issue. Then see what it means for the environment you are responsible for protecting.
Wealth Management & Investing
Cybersecurity, AI governance, technology oversight, and operational controls for firms responsible for protecting client information.
Healthcare & Life Sciences
Secure IT, cyber resilience, privacy, availability, and risk management for environments where technology can directly affect care and continuity.
Manufacturing
Cybersecurity and managed IT where downtime, identity compromise, supply-chain exposure, and system availability directly affect production.
Government
Security, IT resilience, vulnerability management, incident response, and accountability for public agencies and organizations operating under scrutiny.
When the Issue Becomes Your Issue.
Reading about a security threat, compliance requirement, technology problem, or emerging risk is one thing. Working through what it means for your organization is another. Bring us the problem. We’ll help you determine the way forward.
Start the Conversation
Give us a little context and we’ll connect you with the right person at TorchLight.