Continuous Vulnerability Monitoring
Always-on visibility into your security posture, not just an annual snapshot.
Your Pen Test Shows Vulnerabilities Today. What About Tomorrow?
Penetration testing gives you a point-in-time assessment. But threats don’t wait for your next annual test.
New vulnerabilities are discovered daily. Configurations drift. Systems get added. Patches get missed.
Between pen tests, you’re flying blind.
The Solution: Continuous Vulnerability Monitoring from TorchLight
Cloud-based monitoring across all your connected endpoints. Get continuous security monitoring with regular reporting on discovered vulnerabilities, configuration issues, and risk-based prioritization.
Your always-on security radar between pen tests.
What You Get
Continuous Vulnerability Assessment
Automated scanning to identify security weaknesses as they emerge.
Configuration Monitoring
Track configuration drift and misconfigurations that create security gaps.
Risk-Based Prioritization
We prioritize based on criticality and your specific environment.
Regular Reporting
Vulnerability reports on your designated schedule with criticality ratings and clear remediation guidance.
Ideal for organizations that:
✓ Conduct annual or quarterly pen testing but need visibility between tests
✓ Need continuous monitoring for compliance or insurance requirements
✓ Want to identify and remediate vulnerabilities proactively
✓ Need ongoing security posture assessment alongside threat monitoring
Why TorchLight
Real People Who Care – Context, guidance, and support, not just automated reports
Security Expertise – Certified professionals (CISSP, OSCP, PCIP) who understand what matters
Compliance-Ready – Reports designed to support audit, insurance, and regulatory requirements
Proactive Protection – Find and fix vulnerabilities before attackers exploit them
Ready To Add Continuous Vulnerability Monitoring?
Latest Insights & Blog
Expert insights on cybersecurity, compliance, and IT strategy.
-
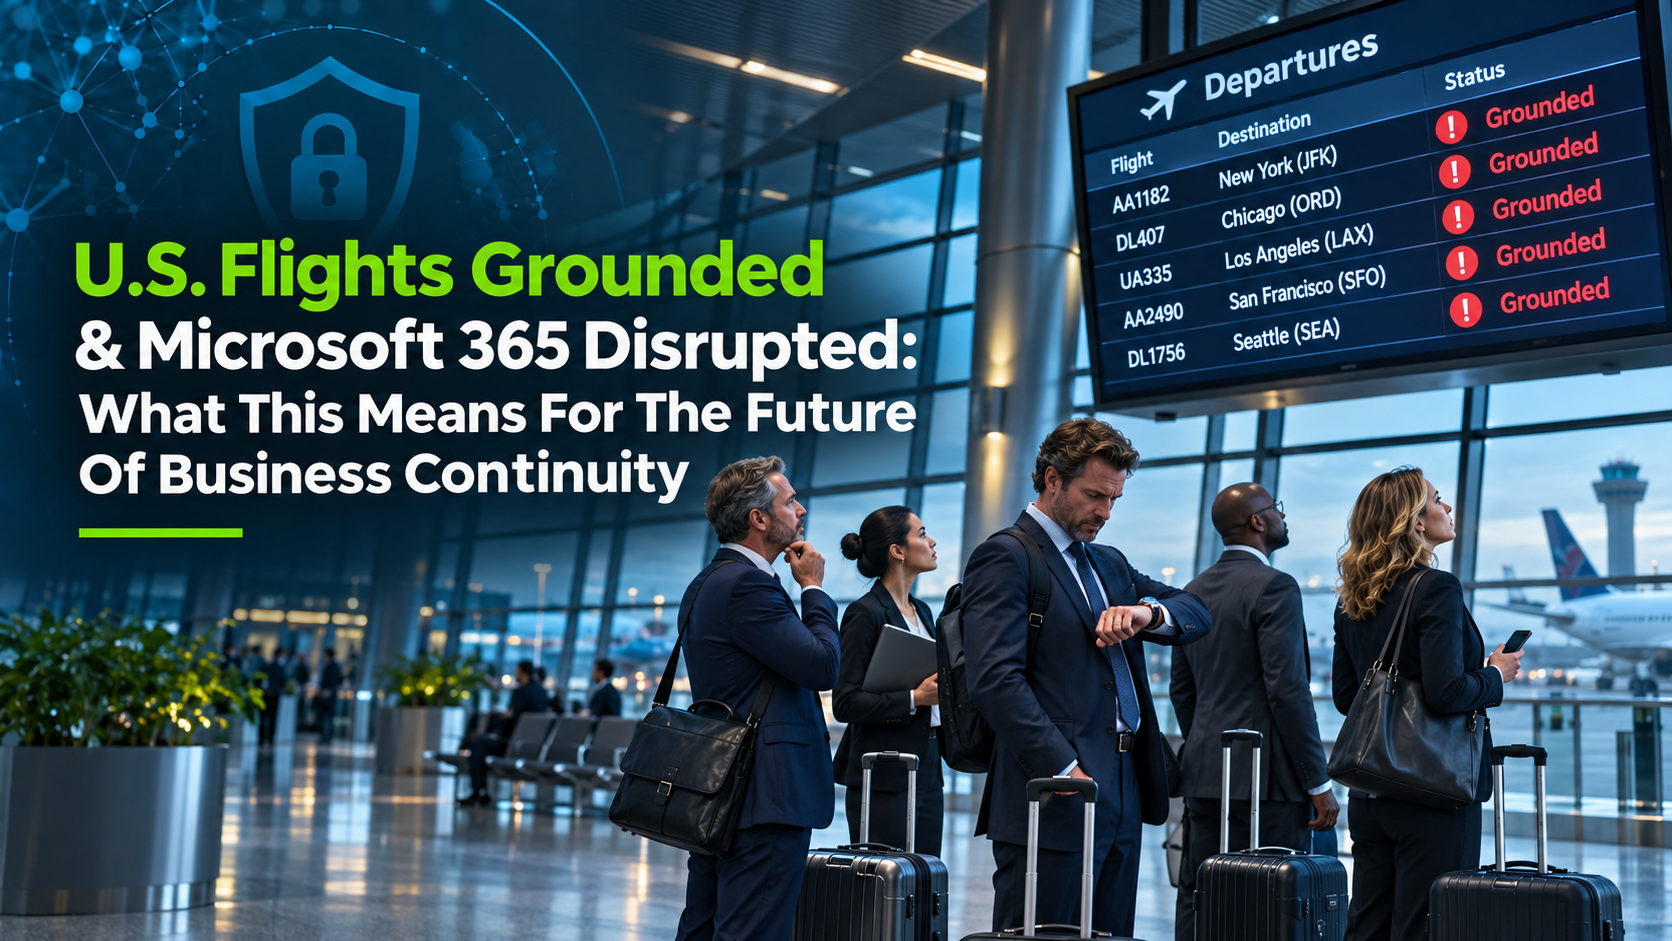
U.S. Flights Grounded & Microsoft 365 Disrupted: What This Means For The Future Of Business Continuity
Two major infrastructure disruptions in less than 24 hours are exposing a critical weakness in traditional business continuity planning. As Microsoft 365 experienced widespread service disruptions and the FAA grounded departing flights nationwide, regulated organizations were reminded that backups and cybersecurity alone cannot guarantee operational resilience. Here’s what business leaders should revisit before the next…
-
Claude Fable 5.2 and Mythos 5.2: What the New AI Capabilities Mean for Business Cybersecurity
Anthropic’s release of Claude Fable 5.2 and Mythos 5.2 demonstrates advances in AI-assisted vulnerability discovery. Combined with Microsoft’s recent findings on automated cloud attacks, the release raises important questions for small and mid-sized businesses. Explore five cybersecurity priorities and a practical 30-day plan for evaluating your organization’s exposure, security monitoring, and readiness. Copy excerpt
-
In-House SOC vs. Managed SOC: What 24/7 Security Really Costs
Hiring another analyst won’t automatically deliver 24/7 cybersecurity coverage. Compare the real cost of building an in-house SOC against managed and co-managed security, using verified workforce research and federal compensation data. A practical 2027 budgeting guide for executives and IT leaders in regulated organizations. Copy excerpt
-
Running Linux? An AI-Developed Exploit Raises New Security Concerns
An AI-developed exploit targeting a critical Linux TCP vulnerability raises new concerns for organizations running Linux servers. Here’s what IT leaders need to know about exposure, IPv4 versus IPv6, patch availability, and protecting critical infrastructure as AI-assisted attacks become more sophisticated.
-
2027 SEC Exam Readiness: The Cybersecurity Evidence RIAs Need
The SEC’s FY2027 exam priorities put RIA cybersecurity, Regulation S-P, third-party risk, and compliance evidence under renewed scrutiny. Discover what investment advisers should document, validate, and prioritize before finalizing their 2027 cybersecurity budgets.
-
Healthcare Vendor Breaches: What Clinics Should Budget For In 2027
Major healthcare vendor breaches involving CareCloud, TriZetto, iRhythm, and Oracle Health exposed risks beyond clinic networks. As healthcare organizations finalize their 2027 cybersecurity budgets, vendor oversight, HIPAA risk assessments, and incident response readiness deserve greater attention. Here’s where clinic leadership should prioritize its investments.
-
CISA Flags Exploited Backup Software: Can Your Business Continuity Plan Survive An Attack?
CISA’s October 2026 warning confirms attackers are exploiting vulnerabilities in backup management software. For CEOs, boards, and IT leaders, the bigger concern is business continuity: Could your organization still recover if both its primary systems and backup infrastructure were compromised? Here’s what leadership needs to know.
-
School District Vendor Risk Management: Why Education Needs Better Vendor Oversight
A school district can secure its own network and still face student-data exposure through a third-party vendor. Using California’s ETS breach as a case study, TorchLight examines vendor risk management, student privacy, and four practical questions school boards should be asking, with specific guidance for Washington and California education leaders.
-
When The Audit Ends, What Happens To Credit Union Member Data?
When an audit ends, sensitive member information may remain with the auditor for years. The Mercadien cybersecurity incident highlights why credit union leaders should review data retention, secure deletion, and vendor notification terms as part of existing oversight.
-
Spokane Public Schools Cybersecurity Incident: What We Know So Far
Spokane Public Schools now says it has reason to believe student and staff data was compromised in the September cybersecurity incident. The investigation remains ongoing as specialists work to determine what information was affected and who may need to be notified.